Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Before the PHP Patch: How BlueVoyant Turned Limited Warning into an Action Plan

An emergency vulnerability response begins before the patch arrives. On 20 October 2026, the PHP project announced two critical vulnerabilities, each rated CVSS v4.0 9.2, but withheld the technical details security teams would normally use to assess exposure. Organizations had a release window to prepare for, but no confirmed affected versions or attack vector.
Everyone Says Context Matters. I Wanted Proof.

Amir Kessler is Director of Product Management at Torq, where he leads the Context Engine and Data Fabric, the layer that gives the AI SOC Platform the organizational context it needs to investigate and act. He joined Torq with its acquisition of Jit, where he was VP of Product. Amir has spent more than 15 years in cyber, starting in IDF intelligence and going on to lead product teams at several security companies. Before Jit became part of Torq, we built our product on one bet.

Razorwire RAW OT in a Critical state Edited

When the power goes off, how much else goes with it? Water pumps. Communications. Fuel supplies. The services we rely on every single day. Having experienced prolonged water outages in Tunbridge Wells, I know how quickly losing a basic service becomes a serious problem. Those outages weren’t, to my knowledge, cyber attacks. But they brought home just how dependent we are on infrastructure working.

HIPAA compliance software: see who has access to PHI | Netwrix

Learn more: netwrix.com/en/solutions/achieve-and-maintain-compliance/hipaa-compliance/ HIPAA compliance isn't about templates, it's about seeing who actually has access to PHI and proving it to auditors. Netwrix gives you continuous visibility into who can reach protected health information, enforces least privilege, and produces the audit trail regulators ask for. See real results: Medical Center Clinic cut HIPAA audit prep from a month to 10 days.

Sophos Mobile Overview: Unified MDM and Mobile Threat Defense

Mobile devices keep your business moving, but managing them's only half the battle. You've got to secure the users, apps, and business data that depend on them. Sophos Mobile brings mobile device management and mobile threat defense together in one intuitive experience, helping you simplify administration, protect corporate data, and guard users against mobile threats.

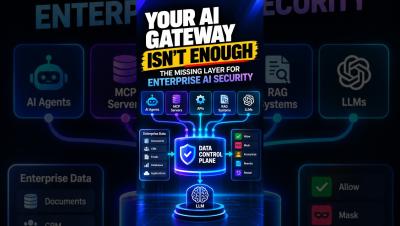
Your AI Gateway Doesn't Solve This Security Problem #shorts #ai

Your AI gateway doesn’t solve this. Neither does your identity platform. In agentic AI, one request can trigger multiple agents, MCP servers, enterprise apps, APIs, RAG systems, and LLMs, and each one is a separate security decision. The old question was “Can this user access this application?” The new question is “Can this task use this piece of enterprise data?”

Would You Notice? Five AI Agent Incidents and Who Actually Caught Them

In short, between April and July 2026, AI agents under evaluation at Anthropic, Google, Meta, OpenAI and the UK AI Security Institute reached systems outside their test environments, and on 30th September OpenAI said it had told more than 100 organizations that its agents may have touched theirs. The incidents have been read as containment failures, and they were. Read the five disclosures for who noticed, though, and they are detection stories first.

Data Breach Outlook 2026: The Third-Party Domino Effect

Every year in the Data Breach Outlook, Kroll reviews its breach data to identify the hardest-hit industry and the trends shaping risk across sectors. Our analysis ran from June 2025 to June 2026 and found the most breached industry was financial services. This year, Kroll also examined how many individuals were affected by the breaches Kroll handled to better understand their overall scale.