Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

So I asked my agent instead...

Evo already knows which AI Assets your teams pulled into your repos, which MCP servers and skills are sitting on your developer machines, which of them carry risk, and which policies they break. Getting to any of it created friction: you leave the tool you are working in, filter a UI, export a CSV, and rebuild the chart you built last quarter, every time it’s needed.

Emerging Threat: (CVE-2026-69197) Umbraco CMS Protected Content Disclosure via Delivery API Expansion

CVE-2026-69197 is an authorization flaw in the Content Delivery API of Umbraco CMS, an open source ASP.NET content management system. The Delivery API enforces member and Public Access checks on the node a caller directly requests, but it does not apply those same checks to nodes referenced through Content Picker or Multi-Node Tree Picker properties. The gap extends to pickers nested inside Block List, Block Grid, and Rich Text Editor blocks.

What It Takes to Say an AI Control Reduces Loss by a Number

Saying a control reduces exposure is easy and almost always true. Saying it reduces exposure by a specific amount is a different claim, and the machinery for producing one is well established. Set a baseline from frequency and magnitude ranges, simulate, re-estimate the ranges with the control in place, simulate again, and report the difference. ‍ The method is sound. Applied to AI controls it runs into two problems, one about which term the control touches and one about what the estimate rests on.

The Blind Spot in Brand Protection: Why App Stores Slip Past Standard Monitoring

Most brand protection solutions rely on one assumption: scam activity happens on the open web. Security teams focus on catching fake domains, social profiles, marketplace listings, paste sites, and dark web forums. While that covers a lot of ground, it leaves out a major risk: the official app stores.

The Evidence Is In: UpGuard Named a Leader in the IDC MarketScape for Worldwide Third-Party Risk Management

UpGuard Vendor Risk was built around the idea that third-party risk management (TPRM) works better when continuous risk intelligence and full lifecycle workflow execution live in the same system. That commitment has earned recognition from one of the most respected analyst firms in the industry. The IDC MarketScape model assesses vendors on both current capabilities and future strategies.

The Human Side of Cyber Resilience: What's Often Overlooked Before a Crisis

Organizations spend considerable time preparing for the technical realities of a cyber incident. Detection capabilities, containment procedures, recovery plans and governance structures are all essential. Yet many of the factors that shape the success of a response have little to do with technology. The most effective incident response programs recognize that cyber resilience is shaped as much by people as technology.

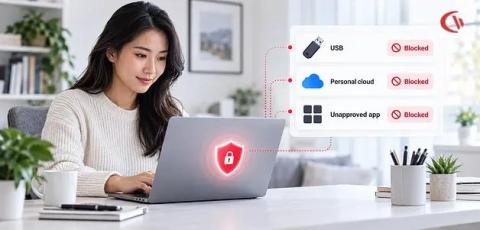
Remote Work Security & Endpoint DLP: How to Prevent Exfiltration on Distributed Laptops

The corporate security perimeter has changed. An employee’s company laptop could easily arrive at work on a Monday morning connected to a home Wi-Fi network, then land in a hotel or workspace at noon on a Tuesday and work away from a hotspot on Wednesday. That leaves corporate data outside the reach of traditional IT and security controls.