Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cash App Scams: How to Spot Them Before You Lose Your Money

Cash App makes sending money instant — and that's exactly what scammers are counting on. Once a payment goes through, getting it back is nearly impossible. In this video, we break down the most common Cash App scams circulating right now: fake support agents, phishing texts and emails, payment reversal tricks, crypto investment fraud, and fake giveaways.


How Early Action Helps Organizations Stay Ahead

In a rapidly changing technology landscape, waiting for consensus can mean losing the advantage. Elisa Costante, VP of Software Engineering at Forescout, explains how acting early helps organizations build understanding, adapt to change, and stay ahead as AI transforms cybersecurity for defenders and attackers alike.

Endpoint Protector picks up 8 G2 badges for Fall 2026

Netwrix Endpoint Protector earned 8 G2 badges in the Fall 2026 reports, including Leader recognition in Data Loss Prevention (DLP) and Data Security, plus Regional Leader and High Performer badges across multiple regions. Endpoint Protector holds a 4.5 out of 5 rating from more than 160 G2 reviews, driven by feedback on fast support, quick implementation, and consistent policy enforcement. Buyers evaluating DLP tools have to take a lot on faith.

Best practices: How to implement Kerberos authentication correctly in your AD environment

Authentication configuration issues, especially those tying into Kerberos, are a big call driver for the Active Roles by One Identity Support team. When Kerberos requirements are met, Integrated Windows Authentication typically attempts Kerberos before falling back to NTLM. Due to expected IIS functionality, we will see multiple HTTP requests which trigger authentication repeatedly.

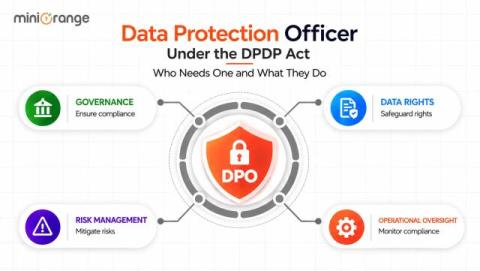
Data Protection Officer Under the DPDP Act: Who Needs One and What They Do

Not every organization that processes personal data has to appoint a Data Protection Officer. Under India's Digital Personal Data Protection Act, 2023, this duty applies only to Significant Data Fiduciaries (SDFs), a category the government assigns based on the scale and sensitivity of the data an entity handles. So before you assume your business needs a data protection officer, it helps to know exactly where this obligation begins and ends.

Passwordless Authentication and Passkeys: How FIDO2 Enables Secure Login

Password-based authentication is slowly disappearing from the login experience in 2026. Instead, users increasingly authenticate with a fingerprint, device PIN, or security key without typing a password. This is where passwordless authentication and passkeys come in. Built on FIDO2 and WebAuthn, passkeys use cryptographic credentials to make passwordless login simpler for users while reducing exposure to phishing and credential theft. But passkeys are only one part of the picture.

What Is a Security Token? How Does It Work?

A security token is a physical device, digital object, or software credential that helps verify a user's identity before granting access to a system, application, network, or account. Depending on the type, it can generate a one-time password (OTP), store cryptographic credentials, or work with an authentication system to prove that the person requesting access possesses the authorized token.

"Better than the tools we were quoted six figures for": How Tines' finance team built a custom billing app for <$1,000

At Tines, Salesforce and NetSuite form our core finance and billing stack. But anyone using these tools will be familiar with the issues this set-up presents — it requires manual, time-consuming work to connect data across the two platforms. Over the years, my team evaluated a bunch of solutions to this problem, including third-party tools and NetSuite’s own native offering.

One Image to Root Them All - The 443 Podcast - Episode 388

This week on the podcast, we break down how a heap overflow in an image-decoding library nobody thinks about became a pull request inside OpenAI's internal monorepo. Three researchers chained it with an OpenAI single sign-on flaw to hijack employee ChatGPT and Codex accounts in under 72 hours; and had an AI write the exploit for them. Before that, we cover the actively exploited maximum-severity authentication bypass in Cisco's Identity Services Engine. Then we close with RatHat, a new Android malware that enables Wireless Debugging, reads its own pairing code from the screen, and asks a commercial AI assistant where to tap.