Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Top tips: How to spot a scammer pretending to be your boss

Top tips is a weekly column where we highlight what's trending in the tech world and share practical ways to navigate these shifts. This week, we're looking at spear-phishing: how cybercriminals weaponize social engineering, why your natural instinct can act as a security blind spot, and practical steps to verify suspicious requests before you take action. I would like to make a confession: I’m a well-versed tech expert, but I almost fell for a phishing scam.


Why Business Leaders Need a New Response Model to AI-Enabled Incidents

Originally published by Cybersecurity Insider. Over the past decade, cybersecurity threats have evolved from a technical issue into a key driver of business and operational risk. Artificial intelligence is accelerating that shift even further, changing the game once again. In 2026, AI in cybersecurity is multifaceted: a tool for defense and incident response, but also a powerful accelerator for attackers. AI-enabled incidents rarely stay contained within the security function.

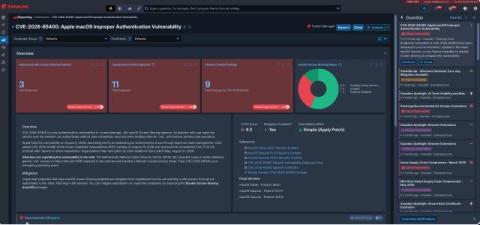
Critical macOS Screen Sharing Authentication Bypass - Under Active Exploitation (CVE-2026-65400)

On August 6, 2026, Apple shipped an emergency, out-of-band fix for CVE-2026-65400, an authentication issue in screensharingd, the daemon behind Screen Sharing, macOS's built-in remote desktop service that listens on TCP port 5900. Apple's advisory describes an attacker who could reach the service over the network and authenticate without valid credentials, then read and write files as root—enough to achieve full remote code execution.

Ship a Working Detection Pipeline in One Workshop: Headless SOC with Grid by LimaCharlie

By the end of this hands-on workshop, you will have deployed a working detection pipeline, ingested a cloud log source, and shipped a bespoke dashboard app, all using Claude Code integrated with Grid by LimaCharlie. Along the way, you will see how Grid compresses the traditional SIEM/EDR/SOAR stack into a single automated workspace. We go well beyond standard EDR and SIEM use cases. What to expect.

Run continuous compliance with Vanta

Plenty of tools can check a box at audit time. Vanta runs continuous compliance, so you're secure every day, not just the week before your audit. It runs on the Trust Graph, Vanta's data and intelligence layer that connects 400+ tools across your stack (cloud platforms, identity providers, task trackers, and more) and gives specialized agents the context to automate accurately. The difference isn't how many tools you connect. It's what happens after. In this video, you'll see Vanta in action.

The guide to HIPAA regulations and rules for healthcare companies and their vendors

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.