Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell: Exposure and Response with the CrowdStrike Falcon Platform

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) introduces two critical remote code execution vulnerabilities affecting PHP, making it important for security teams to identify affected systems, understand their exposure, and investigate potential exploitation.

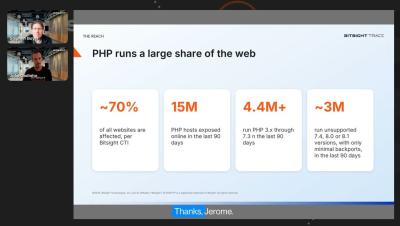
PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

Could PHP2Shell become the next Log4j-scale cybersecurity threat? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. In this webinar, Bitsight cybersecurity experts examine the potential impact of PHP2Shell, share findings from Bitsight's latest exposure research, and explain how security teams can identify vulnerable assets, assess third-party risk, and prioritize remediation.

Patching at the Speed of Mythos

Can you move faster without risking downtime? Mythos is putting pressure on IT teams to patch in days, not weeks. But September's Patch Tuesday was a reminder that speed comes with its own risk: what happens when the patch you need to deploy quickly is the thing that causes an outage? In this session, we'll unpack what September taught us about faster patch cycles and look at how teams can shorten remediation timelines without giving up the testing and control that keep production running.

Tanium Certified Operator: 2026 Refresh: Tanium Tech Talks #174

The refreshed Tanium Certified Operator (TCO) exam swaps simulations for concept-based Q&A. See what changed, what didn’t, and how to prep. The TCO is the foundational Tanium exam: testing whether you understand the basics of interacting in Tanium. This episode covers what changed in the latest cert refresh, what stayed the same, which version to take, and how to prepare.

Vibe Coding Has a Security Problem (And How to Fix)

I vibe coded a working app in 10 minutes without writing a single line of code. It ran fine. It also had a hardcoded API key, a database password sitting in a Model Context Protocol (MCP) config file, and an npm package I never checked. In episode one of Secure Vibe Coding, we look at what AI-assisted coding means for secrets security, using data from GitGuardian's State of Secrets Sprawl 2026 report.