Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is Identity Manager? | One Identity | IGA

What is One Identity Manager? It’s an identity governance and administration (IGA) solution that automates user provisioning, access requests, access certification, and role management across on-premises, hybrid, and cloud environments. Watch this overview to see how Identity Manager helps you enforce least privilege, close compliance gaps, and manage the full identity lifecycle from joiner to mover to leaver. Learn more about identity governance and administration at oneidentity.com.#IGA.
Insider Risk Is Only Scary in the Dark | Teramind Halloween

Some offices are haunted. Not by ghosts, but by everything they can't see. Outdated policies. Silent alerts. No clear view of who has access to what. Systems left wide open. And an audit on the way. This Halloween, Timmy turns on the lights. Watch a haunted office transform as Teramind brings full visibility to every corner of the organization.

Introducing Persona AI: AI for identity operations

Persona AI brings AI directly into the Persona identity platform. It helps teams verify identities, review cases, investigate fraud signals, and apply their own policies to make faster, more consistent decisions. Many identity decisions still need people to do the work by hand: collecting evidence, screening, flagging risk, interpreting policy and routing cases. Persona AI is built into the platform, so it works directly with your identity data, risk signals, policies and workflows.

Falcon Exposure Management Validation Agent: Demo Drill Down

As frontier AI accelerates exploit development, security teams need more than vulnerability severity scores to determine what demands attention. They need evidence of what can actually be exploited. In this demo, see how the CrowdStrike Exposure Validation Agent uses frontier AI to generate exploits for supported CVEs and test them in a controlled lab environment. Explore how Falcon Exposure Management evaluates exploitability conditions, documents attack prerequisites and potential impact, and provides evidence of successful exploitation.

Skip Trace: Delivering NDR without the Complexity | WatchGuard Webinar

Network Detection and Response (NDR) has traditionally come with a heavy price tag, including complex deployments, expensive infrastructure, constant tuning, and skilled analysts to manage the workload. That model was built for enterprise SOCs, not MSPs protecting dozens or hundreds of customers.

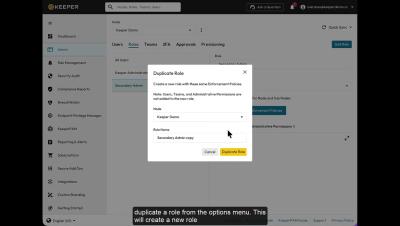
How to set up role-based access controls in Keeper's Admin Console

Learn how to set up role-based access control (RBAC) in Keeper Security’s admin console. This video covers the difference between Roles and Teams, how the default Keeper Administrator and All Users roles work, how to add a role and configure its enforcement policies, and how to duplicate a role. It also covers how to delegate administrative permissions by node, including how Cascade Node Permissions applies those rights to sub-nodes.