Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

FBI Releases Flash Alert on Netwalker Ransomware

The Federal Bureau of Investigations (FBI) released a flash alert in which it warned organizations about the dangers of Netwalker ransomware. On July 28, the FBI revealed in Flash Alert MI-000130-MW that it had received notifications of attacks involving Netwalker against U.S. and foreign government organizations along with entities operating in the healthcare and education sectors.
Announcing Veracode Security Labs Community Edition

We recently partnered with Enterprise Strategy Group (ESG) to survey software development and security professionals about modern application development and how applications are tested for security. The soon-to-be-announced survey found that 53% of organizations provide security training for developers less than once a year, which is woefully inadequate for the rapid pace of change in software development.

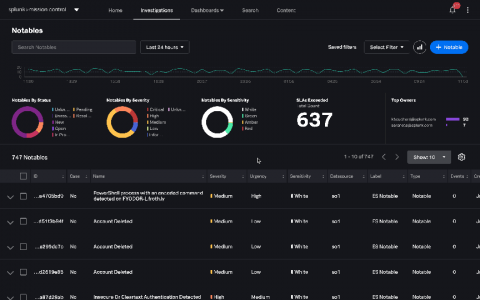
A Unified Security Operations Platform: Splunk Mission Control

Security is easy, right? Get yourself a patchwork of security point products meant to solve one or two specific problems, and your organization is safe from threats! Ah, if only it were that simple… In reality, security operations are disjointed and complex. Security visibility and functionality (i.e. threat detection, investigation, containment and response capabilities) are often divided among a multitude of different security products (e.g.

New Redscan FOI report reveals the state of cyber security across UK universities

In March 2020, Redscan sent Freedom of Information (FOI) requests to 134 universities across the UK. The aim was to understand more about the frequency of data breaches in the sector and some of the steps institutions are taking to prevent them. The focus on universities was due to the integral role these organisations play in conducting world-changing research and shaping the skills and knowledge of the workforce. The results of the FOI request are available to download in a short report.

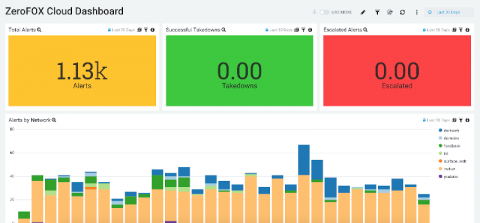
Sumo Logic and ZeroFOX Join Forces to Improve Visibility and Protect your Public Attack Surface

Today’s organizations have the challenge of managing several different applications and software within their technology stack. The more public-facing platforms an organization utilizes, the greater their public attack surface risks. Without proper protection, they and their community can become an easy target for malicious actors.

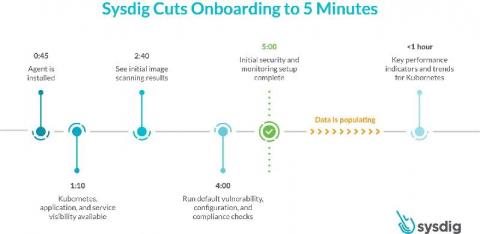
Sysdig cuts onboarding for container and Kubernetes visibility and security to 5 minutes

Today, we are excited to announce a faster onboarding for Kubernetes visibility and security. With the SaaS-first approach and new enhancements to the Sysdig Secure DevOps Platform, you can get results after just a five-minute setup. This release includes a new guided onboarding process, out-of-the-box dashboards as part of curated essential workflows, and a new Sysdig Essentials tier. 5 minutes to onboard secure DevOps - YouTube An error occurred.

Google Chrome Aims to Keep its Edge Over Other Browsers with its Latest Privacy and Security Features

Google Chrome may currently enjoy the numero uno position in the world of browsers, but it is starting to feel the pressure. The competition is heating up with its rivals like Microsoft Edge offering upgraded security features to lock in more users. The coronavirus pandemic has brought extensive changes to the way people operate, which in turn, has created a need for securing remote workforces.

Introducing the Egnyte Content Services Platform

Today, we are excited to be launching the Egnyte Content Services Platform, the evolution of our industry-leading content collaboration and data governance technologies, to help organizations address the issues they face and allow for effective deployment of secure content services. The Platform is a major step forward in the progression of how companies create, use, transact, and manage their critical data.