Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

5 Top Container Image Security Platforms for 2026

Technology changes every year, and one of the biggest shifts over the last decade has been a deep investment into the use of containers. Containers offer a lot of potential benefits, particularly for information security, but they also present serious risks of their own. Those risks can be mitigated, but you need to understand that the problem exists before you can address it.
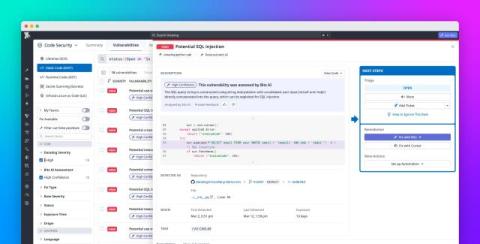
Introducing our open source AI-native SAST

Static application security testing (SAST) tools help developers quickly catch potential vulnerabilities as they code. However, these tools rely on inflexible rules that often generate a high number of false positives, reducing trust in their accuracy and slowing adoption. To help developers access context-aware vulnerability detection, we’ve released an open source AI-native SAST solution. This tool scans code changes incrementally and surfaces security issues in real time.

How AI is changing IGA

It’s no surprise that AI is being integrated into identity governance and administration (IGA) platforms. Automation promises productivity boosts, risk detection can be in real-time and cloud environments allow greater scalability. What’s more, the pace of AI means IGA is quickly moving beyond slower, more rigid, rule-based approaches.

Exploring Active Roles RBAC solution for streamlined permissions management

Despite constant sweeping changes across IT, Active Directory (AD) continues to be the center of identity and access management (IAM) processes for most enterprises. Even as organizations adopt cloud identity platforms, on-premises AD carries the lion’s share of user authentication, authorizing access to critical systems and anchoring hybrid identity strategies. Because of this central role, AD security is nearly inseparable from directory security, cyber-resilience and breach prevention.

New Strategies to Automatically Block Website Ping Attacks

Protecting websites from cyberattacks remains critical. One common type of attack is the Ping Flood, which is different from the historical ‘Ping of Death.’ This is when many ping requests are sent to a website's server at once, slowing it down or even crashing it. As web traffic and application complexity increase, exposure to denial-of-service attacks grows. This is why it's important to have strong defenses in place.

From Zoomin to Fluid Topics: Evolving the Securonix Documentation Experience

By: Mark Johnson, Manager, Knowledge Engineering You’ve heard it said: “The more things change, the more they stay the same.” Well, sometimes, everything changes and you don’t even notice! This just happened. The Securonix Documentation Portal changed completely, and everything looks the same! (Well, almost.) A few years ago, Securonix set out to modernize how customers interact with product documentation.

Your AI SOC still needs a SIEM. Here's why that won't change.

Everyone is building sophisticated intelligence layers with improved models and smarter agents to automate threat detection, investigation, and response. It’s what is needed in order to mature into an AI SOC. However, the organizations seeing the most value from AI in their SOC are not focusing solely on the intelligence layer. They’re focusing on the data foundation first.

Weekly Cyber Security News 09/04/2026

Let’s catch up on the more interesting vulnerability disclosures and cyber security news gathered from articles across the web this week. This is what we have been reading about on our coffee break! Thankfully this common WP Plugin is well patched by now, but of course there will always be some who don’t enable auto-updates… But its better late than never for this one: Interesting, Rowhammer has migrated to the GPU.