Nvidia Hit with Cyberattack, Proprietary Data Stolen
Read also: Toyota suspends production due to a cyberattack, Enercom suffers satellite outage, and more.


Read also: Toyota suspends production due to a cyberattack, Enercom suffers satellite outage, and more.
Here in the United States, we often focus on the cybersecurity readiness of the federal government. The reality is that state and local government departments are just as, if not more vulnerable to cyber attacks. Nearly one quarter of their employees use personal devices for work, where security teams have little visibility, enabling threat actors to execute phishing and other malicious activities. These risks will only continue to grow as in-person services continue remotely.
Microsoft engineers shared that 99.9% of compromised accounts forgot to turn on MFA. Despite so many warnings and proof of the efficacy of MFA, an M365 security report by Coreview reveals that 78% of M365 administrators do not have MFA activated. Isn't that crazy? It's not always perfect (phishing, social engineering and password brute-force attacks, device theft etc.); nevertheless, it is clearly better than not having it. However, if not implemented with care, it can create headaches for MSPs.
Software-as-a-service (SaaS) has taken over the world because it’s easy. With just a few clicks, business units can find an application that’s suitable for a particular business process. They can subscribe to it and immediately start using it — and the IT department might never find out.
The US Senate has passed legislation designed to improve the cybersecurity of the Federal Government. The legislation, which consists of three bills, was unanimously passed by the Senate on Tuesday evening, and would – amongst other things – require organisations working in critical industry sectors to alert the US Government about hacks and ransomware attacks.
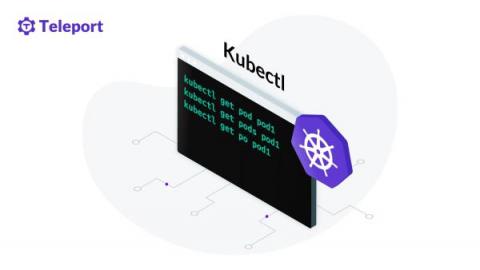
In the last few years, Kubernetes has grown exponentially in popularity. Its wide adoption can be attributed to its open source nature, flexibility, and ability to run anywhere. Developers also love the fact that you can manage everything in Kubernetes using code. kubectl is the Kubernetes-specific command line tool that lets you communicate and control Kubernetes clusters. Whether you’re creating, managing, or deleting resources on your Kubernetes platform, kubectl is an essential tool.
Beyond the disturbing images of the invasion of Ukraine that began February 24 are the invisible cyberattacks that preceded it and continue to be waged on Ukraine by Russian state-sponsored and other threat actors, which also threaten the West. Vedere Labs, Forescout’s threat intelligence and research team, is closely monitoring the evolution of cyber activities connected to the Russian-Ukrainian conflict.
Cloud Infrastructure Entitlements Management (CIEM) is a cloud security solution used to manage identities and cloud permissions through the principle of least privilege (POLP). CIEM uses machine learning and analytics to detect anomalies in account permissions within multi-cloud environments.
A reverse proxy server (or reverse proxy) facilitates a user’s requests to a web server/application server and the server’s response. A load balancer receives user requests, distributes them accordingly among a group of servers, then forwards each server response to its respective user. From the brief definitions above, it’s clear that reverse proxies and load balancers have some overlapping functionalities.