Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Quantifying OT Cyber Risk Without a Loss History

Quantifying cyber risk in an enterprise IT environment starts from frequency. Incidents of a given type happen at some rate, that rate is observable across enough organizations to be estimated, and severity follows from what was affected. ‍ Operational technology inverts both halves. Frequency data barely exists, and the consequences are already documented in detail by people who have never thought about cyber. Working with that inversion rather than against it is what makes the modeling tractable.
The guide to HIPAA regulations and rules for healthcare companies and their vendors

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

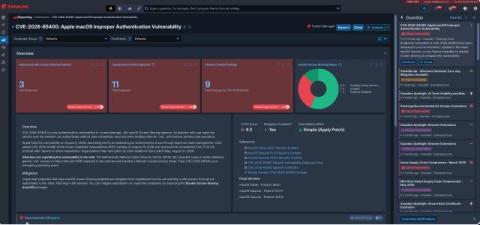
Critical macOS Screen Sharing Authentication Bypass - Under Active Exploitation (CVE-2026-65400)

On August 6, 2026, Apple shipped an emergency, out-of-band fix for CVE-2026-65400, an authentication issue in screensharingd, the daemon behind Screen Sharing, macOS's built-in remote desktop service that listens on TCP port 5900. Apple's advisory describes an attacker who could reach the service over the network and authenticate without valid credentials, then read and write files as root—enough to achieve full remote code execution.

Why Business Leaders Need a New Response Model to AI-Enabled Incidents

Originally published by Cybersecurity Insider. Over the past decade, cybersecurity threats have evolved from a technical issue into a key driver of business and operational risk. Artificial intelligence is accelerating that shift even further, changing the game once again. In 2026, AI in cybersecurity is multifaceted: a tool for defense and incident response, but also a powerful accelerator for attackers. AI-enabled incidents rarely stay contained within the security function.

MSP Central expands its security stack with Device Control

MSPs are maturing endpoint security with patching, vulnerability remediation, and antivirus protection. But one high-impact risk still slips through in many client environments: unmanaged peripheral devices. A single unauthorized USB drive can copy sensitive client data in minutes and introduce malware into otherwise protected systems. This is why we've launched Device Control in MSP Central—an MSP-ready solution capable of governing every device that touches your client endpoints.

7 API Security Requirements for Payment Transactions

Every payment flow your organization runs, from card authorization to ACH transfers to embedded lending to open banking consent, is now an API call. That’s good for velocity. It’s also why payment APIs sit at the top of the attack surface for financial services and enterprise SaaS platforms handling money movement.

Focus on the Threats That Actually Matter to your Organization with Sectoral Intelligence

Not every threat matters equally to every organization. A newly discovered APT or ransomware group targeting European automotive manufacturers is definitely worth paying attention to, especially if you’re in that sector. But if you’re a financial services firm in California, it’s probably not an immediate priority. You might look into it, track its activity, and assess whether it could become relevant.

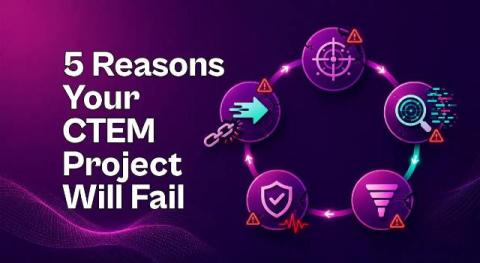
5 Reasons Your CTEM Project Will Fail

CTEM sounds straightforward as a five-stage loop, but most programs stall quietly somewhere inside it. This post breaks down the five places CTEM projects actually break — bad scoping, unreconciled discovery tools, severity mistaken for risk, skipped validation, and unowned remediation — and argues that these aren’t five separate problems, but symptoms of running CTEM as disconnected efforts instead of one continuous workflow.