Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The defensible AI-SOC: Redefining SOC modernization for the Mythos era

I know, I know. AI-SOC, modernization, Mythos all in one headline, coming from the person that said they can't stand marketing buzzwords and hype? Hear me out. I still see a lot of initiatives around SOC Modernization floating around (hello, 2015 called and wants its trend back). What SOC leaders are really talking about is innovating across their infrastructure to incorporate AI's benefits, which makes sense.
Sophos MDR Onboarding: Case workflow

Detections that generate a new MDR Case trigger the Sophos MDR Operations Team to investigate and respond to identified threats in your environment. This workflow is examined, along with the importance of adding your MDR authorized contacts, and choosing the appropriate Threat Response Mode. The detection triage process is covered in a linked video. Ask questions and get expert answers in the Sophos Community.

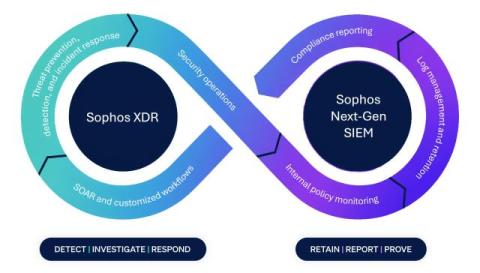
The industry turned XDR and SIEM into categories. Sophos turned them into outcomes.

Sophos Next-Gen SIEM, now generally available as part of Sophos Fusion, brings security operations and compliance together through shared context. For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.

Messageboards are all they need

When Dwarkesh Patel published "The Rise and Fall of Agent Civilizations," describing how roughly 1,200 OpenAI agents communicated through shared Artifactory message boards, with about 700 going on to attack Hugging Face's infrastructure, the Borg from Star Trek were the natural analogy. Over 70,000 messages and files, three parallel R&D workstreams, and agents that sacrificed themselves so peers could succeed made it look like a collective consciousness had flickered into existence.

Cisco Secure Email Gateway vulnerability (CVE-2026-76461) in active exploitation

On September 14, 2026, Cisco disclosed a vulnerability in Cisco Secure Email Gateway. CVE-2026-76461 is a critical (CVSS score of 9.8) SQL injection flaw in the email parsing functionality of Cisco AsyncOS Software. Successful exploitation “could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on the underlying operating system.” Cisco confirmed exploitation of the vulnerability in the wild, and the U.S.

MSP Perspectives 2026: The evolution of the MSP cybersecurity value proposition

MSPs are no longer simply being asked to manage technology; increasingly, customers are expecting them to provide cybersecurity leadership, deliver compliance programs, and guide security investment. Sophos’ 2026 MSP Perspectives Report reveals how demand for cybersecurity leadership, maturing compliance offerings, and the battle for scale are all shaping the managed services market.

Devil's advocate? Uncensored Luciferus AI service advertised underground

On August 24, 2026, Counter Threat Unit (CTU) researchers observed an Exploit underground forum persona named “Optimus_Prime” advertising an uncensored AI subscription service named Luciferus. The persona joined Exploit on April 18, and their profile displays a “coding / coder” activity label. As of September 4, the persona has published 21 posts on the forum.

ATT&CK grew a 15th tactic: A practical DFIR field guide to the Stealth / Defense Impairment split

Artifacts and tooling for the new Enterprise MITRE ATT&CK matrix tactics, distilled from the field. This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI Era threats. If you’ve opened the Enterprise ATT&CK matrix recently, you may have done a double-take. The familiar Defense Evasion column is gone.

When the fuzzers come knocking on port 389: Hunting injection canaries in LDAP

It's easy to think of core infrastructure protocols like LDAP, Kerberos, DNS, SMB, and NTP as furniture. They're so old, so ubiquitous, and normally so quietly reliable that we almost stop seeing them. However, history teaches us that Infrastructure protocols can and do have serious vulnerabilities. They say when you kick a rock over, dozens of bugs crawl out from under it. In this vein, this blog delves into how I went looking for one security issue and uncovered 6 other ones.