Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

7 AI Detection and Response Platforms for Enterprise Security Teams

The most difficult AI incidents do not necessarily begin with an obviously malicious prompt. An employee can ask an approved agent to summarize customer data. The agent retrieves the correct records, invokes an approved tool, generates the requested output, and then sends it somewhere it should never have gone. Every individual action may look legitimate in isolation. The incident only becomes visible when security can reconstruct the entire sequence and understand what the user intended, what the agent inferred, which systems it touched, and where the execution path diverged.

Financial Firm Stops Identity Attack in Under 2 Hours

Developing the full picture of an incident is essential for SOC teams responding to complex threats. A financial firm faced this challenge when attackers created legitimate accounts within their Google Workspace environment. While native alerts flagged the activity, investigators needed deeper context to determine scope and exposure. With Corelight, the team gained the network evidence and chronological activity timeline needed to scope the incident and restore full visibility.

Episode 22 - The CTO's Case for AI: Fixing Bugs, Vibe Coding, and the Future of Dev Jobs

In this episode, host Richard Bejtlich sits down with Steve Smoot, Chief Technical Officer at Corelight, to explore how AI is reshaping the daily work of engineers and defenders alike. Steve traces his path from early employee to CTO and explains why the flexibility of Open NDR—where a simple ten-line Zeek or Spicy script can solve a customer's edge case without a full product release—remains a core advantage. The conversation digs into practical realities of working with large language models.

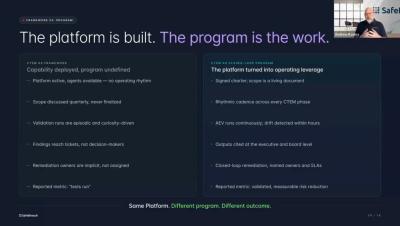
How Do You Operationalize CTEM and Prove It's Working?

Having the right security platform is only part of the equation. Two organizations can have similar security stacks and still achieve very different outcomes depending on how they operationalize their Continuous Threat Exposure Management (CTEM) program. In this video, learn what separates reactive, ad hoc security validation from a mature CTEM program—including: See how a structured CTEM program can turn continuous security validation into measurable progress across your organization.

What Campaigns Like Grandoreiro Teach Us About Threat Detection

The recent Grandoreiro campaign detected by the WatchGuard Threat Lab team is a clear example of how today’s threats combine different techniques to make detection more difficult and operate more discreetly. In this case, the attack begins with a phishing email designed to persuade the user to click a link. From there, the victim is taken through several redirects and eventually downloads a compressed file from well-known services such as Dropbox or MediaFire.

Domain Monitor Now Catches the Impersonation Attempts Keyword Matching Was Built to Miss

Domain Monitor's detection engine has been rebuilt to catch impersonation domains that keyword matching was never built to find. This release covers the new evidence-based matching engine, per-keyword Low, Medium and High thresholds, and what's coming next as the improvements roll out in stages. Domain Monitor's detection engine has been rebuilt from the ground up.

The Art of Detection Engineering: Why Great Detections Are Built with You

Out-of-the-box detection content gives security teams a strong starting point from day one. Its full value emerges when that content is tuned to reflect the users, systems, workflows, and risks unique to your environment. This article walks through why tuning matters, how mature security teams approach it, and how Securonix helps turn expert-built detection content into high-fidelity security outcomes.