Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

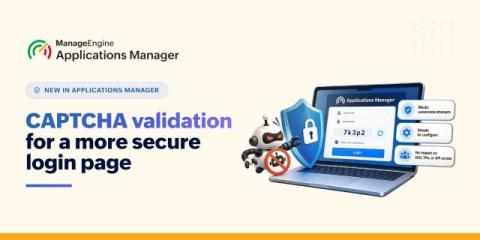
Protect Applications Manager logins with CAPTCHA validation

Login pages are one of the most attacked surfaces of any enterprise tool. They're often internet-facing, they're the front door to sensitive operational data, and unlike most vulnerabilities, they don't need to be discovered—they can simply be targeted with large volumes of automated attempts. For monitoring platforms like Applications Manager, which frequently sit with visibility into critical infrastructure, that front door matters even more.
What's New - September 2026 Release

Discover everything new in the September 2026 update of Acronis Cyber Protect Cloud! This release introduces major enhancements across billing, backup and recovery, security, infrastructure, RMM, MDR, integrations, and partner tools - helping MSPs strengthen cyber resilience, streamline operations, and expand their service offerings. Essential updates covered: Like, comment, and subscribe for more Acronis news!

Acronis Cyber Protect v17: Improving cyber resilience across people, data and infrastructure

Cyber resilience depends on more than recovery. Organizations need to protect critical data, empower users to recognize threats, maintain visibility across IT environments and ensure recovery is available when it matters most. Acronis Cyber Protect v17 Q3 2026 expands integrated cyber protection with new capabilities that strengthen security awareness, improve backup operations and extend protection across more virtual environments.

5 API Risks a Fully Tooled Marketplace Missed: Lessons From a Real PoC

If your team already runs API security tooling, you have probably answered the board’s question with a list: API discovery, testing, runtime protection, bot defense, perhaps a WAF or API gateway in front of it all. Every box is ticked. Yet the honest question every security leader still carries is harder to answer. Is anything getting through? That question has a specific answer, and it rarely comes from the tool inventory.

Put Threat Intelligence to Work

Threat intelligence is easy to find. Turning it into a detection that works in your environment is harder. A new campaign surfaces. Research lands in an inbox, threat feed, or repository. Then the real work starts. Someone has to identify the behaviors worth detecting, find the right telemetry, map the right attributes, build the logic, validate it, and tune it for the environment. That work takes expertise. And in many SOCs, that expertise sits with a small number of detection engineers.

The cyberattack your security team has no framework for

At the opening bell, your stock drops fifteen percent due to a data breach that never actually happened. Fake screenshots, a fake CEO statement, no actual hack. Your security team looks into it, but finds nothing because there's nothing to find. And the damage is already done. Gartner is calling disinformation attacks like this a top threat, and most companies aren’t prepared to handle it. For more insightful videos, visit ManageEngine Insights.

Revoked Isn't Removed: The Supplier Exposure a Federal Ban Leaves Behind

Federal security restrictions and procurement bans have targeted Chinese telecommunications and technology suppliers for years. But removing a company's name from an authorization is not the same as removing the risk it carries into a supply chain. For C-SCRM programs, the harder question is identifying where that risk persists — through affiliates, resellers, data center tenancies, and proxy or sub-tier relationships that no order directly names.

Emerging Threat: (CVE-2026-94483) Next.js Server-Side Request Forgery via Image Optimization

CVE-2026-94483 is a server-side request forgery flaw in the Image Optimization feature of Next.js, the React framework maintained by Vercel. It is classified as CWE-918. Image Optimization fetches a remote image on the server and re-encodes it. Before fetching, it checks the requested URL against the images.remotePatterns allow-list. The flaw is that the allow-list check and the fetch resolve DNS separately, so a host that passes the check can resolve to a different address by the time the fetch happens.