Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

When Cybersecurity Becomes Pay to Play

Awards you have to pay to win, events you have to pay to attend and conferences that expect speakers to work for free. When did recognition and expertise in cybersecurity become something you have to buy? Welcome to Razorwire, the podcast where we share our take on the world of cybersecurity with direct, practical advice for professionals and business owners alike. I'm Jim and in this episode I'm joined by security consultant and regular community speaker James Bore and Gary Hibberd, co-founder of Consultants Like Us and the Real Cyber Awards and Conference.
3 Things CISOs Need to Know About Microsoft's ISOC Announcement

Cost pressure can decide what your security team gets to see. A useful log source gets left out. Investigation history gets shortened. Analysts work with the evidence the organization could afford to keep. That is the part of Microsoft's Integrated Security Operations Center, or ISOC, announcement I keep coming back to. Bringing SIEM capabilities into the Defender experience, using native security data, and changing the economics gives customers a reason to revisit those decisions.

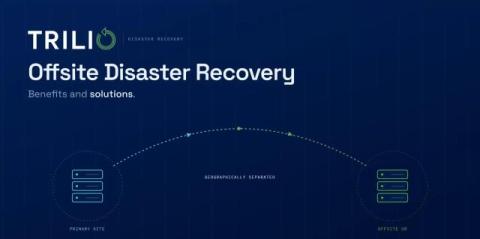
Offsite Disaster Recovery: Benefits and Solutions

Most teams find the holes in their recovery plans at the worst possible time: a flooded data center, failed storage array, or ransomware note sitting on the same server as the backup catalog. Offsite disaster recovery removes that single point of failure, but only when the copy is truly separated from production by geography, network path, and access control. Distance by itself won’t save you.

How Headspace is taming wild code with Tines 3B

One of my favorite parts of my role is working closely with innovative customers like Chris Oh, Senior Director of AI Enablement at Headspace. Chris and I recently caught up to talk through how Headspace uses Tines 3B to give teams the freedom to build with AI, without the operational risk. We covered the problem Headspace set out to solve, why they chose Tines 3B, and some of their early wins with the product.

Cyber Resilience Act is here! Myth busting and first impressions

The first deadline of the Cyber Resilience Act went live last week. The Cyber Resilience Act (CRA) is the new EU regulation that defines minimum cybersecurity requirements for all products with digital elements, including their building blocks (hardware and software). It applies to anyone placing products on the EU market, not just companies based there. The full requirements won’t go into effect until the end of next year.

The Agent Will See You Now: Why Healthcare's AI Agent Boom Needs Visibility and Control

Ask AI to Choose a prompt Write a TLDR of this post Explain the security risk Summarize what CISOs should know Healthcare, as an industry vertical, is moving faster on agentic AI than it has in past technology evolutions. Some reports say it is outpacing other regulated industries. Ambient scribes are documenting patient visits in real time. Prior-authorization and revenue-cycle agents are handling payer workflows that used to require staff to log into multiple systems manually.

What's New - August 2026 Release

Discover everything new in the August 2026 update of Acronis Cyber Protect Cloud! This video highlights the latest features and enhancements empowering MSPs to expand workload protection, strengthen disaster recovery, automate workflows, and improve operational visibility. Essential updates covered: Like, comment, and subscribe for more Acronis news!

The AI-powered GRC team: Scaling compliance, not complexity

GRC teams have invested heavily in building mature control frameworks. But the real challenge? Having the visibility into whether they’re working, where gaps exist, and how to keep them running effectively at scale. As compliance programs become more complex, teams need new ways to move beyond manual processes and maintain confidence in control effectiveness. Join GRC experts from Tines for a conversation with Ayoub Fandi, Founder of GRC Engineer, to learn how leading organizations are reducing manual effort and improving visibility, and building compliance programs that scale.