Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Three expert tips for cultivating secure software development practices

We often hear about the importance of DevSecOps — integrating security into DevOps processes. But as many security professionals know, it’s not nearly as easy as it sounds. Cultivating secure software development practices requires working alongside developers with varying opinions, priorities, and idiosyncrasies. And any process involving humans is complicated. So, how do today’s security teams overcome these challenges and make secure software development practices a reality?
sysctl configuration hardening

Sysctl is a command-line utility in Unix-like operating systems that allows users to view and modify kernel parameters at runtime. These parameters, also known as “tunable” or “kernel” parameters, control various aspects of the operating system’s behavior, such as network settings, memory management, file system behavior, and more. Each of these operating systems has their own implementation of sysctl, with slightly different options and syntax.

Why Your SOC Needs Automated Incident Response

Automated incident response can help security teams identify and respond to cyber threats faster. When a breach happens, delays equal costs. Today, a cyber attack happens every 39 seconds, and the global average total cost of a data breach is the highest it’s been in 17 years. In this environment, a low response time is crucial to reducing cyber risk.

Testing the actual security of the most insecure Docker application

Our previous research on CVE exploitability in the top DockerHub images discovered that 78% of the reported CVEs were actually not exploitable. This time, the JFrog Security Research team used JFrog Xray’s Contextual Analysis feature, automatically analyzing the applicability of reported CVEs, to scan OWASP WebGoat – a deliberately insecure application. The results identified that out of 60 CVEs reported with a Critical CVSS score, only 10 are actually applicable.

Importance of great communication

In all relationships, issues can arise. The key to solving those issues is to have a clear understanding of the issue itself. For instance, when a customer reports an issue it is critical to listen to the customer with patience and empathy so that they feel understood, and to assure them that they will receive assistance promptly. Furthermore, product issues can present themselves in various forms of complexities.

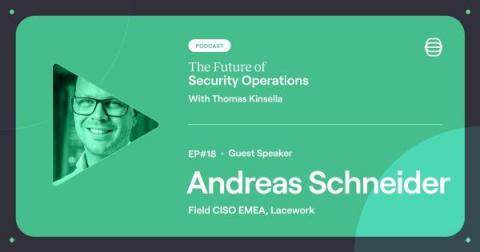
Lacework's Andreas Schneider: How to adapt as a CISO and the value of security failures

In this episode of the Future of Security Operations podcast, Thomas interviews Andreas Schneider - the Field CISO EMEA at Lacework. Leveraging its data-driven platform and cloud-native application protection solution, Lacework helps organizations make sense of immense amounts of security data with minimal effort.