Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

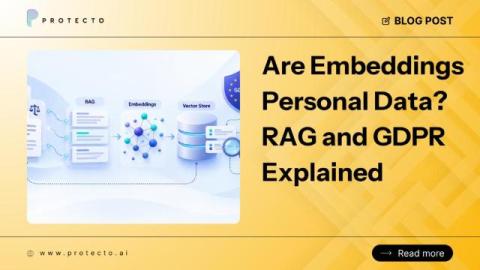
Are embeddings personal data? RAG and GDPR explained

Short answer: Do not assume an embedding is anonymous. An embedding can be matched back to the text it came from, and the text is usually stored right next to it. Treat each representation in a RAG pipeline as personal data when it can still be tied to a person, which is most of the time for chunk text. When the source record is deleted, every copy has to go. Your team builds a RAG assistant over HR policy and customer contracts. Documents go in, get chunked, get embedded, and land in a vector store.
Protect your sensitive data with Cloudflare

Before you paste customer data into an AI prompt… pause for one second. From sales pipelines to customer contracts, RevOps handles sensitive data constantly. Ida Yunos, Revenue Operations Leader for APAC & Japan, explains why good data security habits belong to everyone, not just IT. Watch the video to see how to protect data while keeping daily work moving.

The We're All Gonna Die Episode: AI Doomsday Myths & Real Risks | Attempted Intelligence Ep. 3

Is artificial intelligence really going to end humanity, or are Hollywood tropes distracting us from the actual threats facing enterprise tech today? In Episode 3 of Attempted Intelligence, hosts Harlan Parrott (VP of AI Innovation at KnowBe4) and Matt Duren (SVP of Engineering for AI & Data) investigate the biggest fear surrounding artificial intelligence: the existential doomsday scenario. Using a classic detective framework, Harlan and Matt put the theory on trial by examining whether AI has the means, motive, and opportunity to wipe out humanity.

PHP2Shell is in CISA KEV: why runtime visibility matters

Five days after PHP shipped the fix, CISA added both PHP2Shell flaws to its Known Exploited Vulnerabilities (KEV) catalog. Federal civilian agencies have until October 29 to remediate. Last week’s question was whether attackers could turn the flaws into working shells. This week’s question is which of your images and hosts still run an affected PHP build, and who can fix each one.

Social Engineering Attacks Against Businesses: Examples, Risks, and Prevention

Social engineering attacks differ from other cyberattacks most businesses face. In this type of attack, attackers exploit human trust rather than depending only on technical vulnerabilities. They impersonate employees or business partners to trick people into sharing sensitive information or transferring money. In some cases, they are also granted unauthorized access to company systems.

Kubernetes backup console tour: backup plans, targets, policies | Trilio for Kubernetes

A tour of the Trilio for Kubernetes management console on OpenShift, so you know where everything lives before you create your first backup target and backup plan. You will see: Chapters Recorded on Red Hat OpenShift 4.21 with Trilio for Kubernetes 5.4.1.

What Is Penetration Testing? Types, Stages and How Often to Test

Every business with a website or email accounts has weak spots, and penetration testing helps you find them before an attacker does. Security experts try to break in the way a real hacker would, so you can see whether your defences hold up. The test itself is only the start. How often you test and what happens with what the testers find, decides whether a report makes you any safer. Both are worth knowing before you compare penetration testing services.

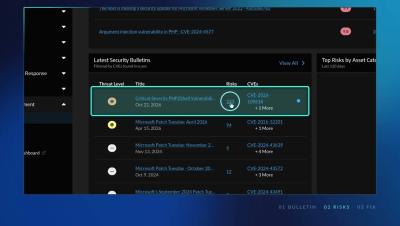
Is My Organization Exposed to PHP2Shell? See It in Aurora Vulnerability Management

PHP2Shell is two unauthenticated remote code execution (RCE) flaws with public exploit code. As AI speeds up the path from vulnerability to exploit, security leaders keep asking two questions. Are we exposed? And what do we fix first? This walkthrough shows how Aurora Vulnerability Management from Arctic Wolf answers both.