Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Sequoia spotlight: Deploying the newest macOS with Endpoint Central

Apple released its new macOS Sequoia 15.0 on Sept. 16, and we at ManageEngine are excited to announce our support from the day of its release. Before we get into the details, let’s look at which devices are eligible for the facelift. Source: Apple Sequoia was unveiled at WWDC 2024 with a range of features around privacy, security, and its much-awaited Apple Intelligence.

Living-off-the-land Attacks: The Challenge and WatchGuard Advanced EPDR

In cybersecurity, "Living-off-the-land" (LotL) attacks have become increasingly difficult to detect. These attacks exploit legitimate system tools like PowerShell, WMI, or Office macros instead of relying on external malware, allowing attackers to move stealthily within a network. Traditional security measures struggle to identify these attacks, as they use trusted, digitally signed tools. LotL attacks appeal to cybercriminals because they evade detection and reduce the risk of being traced.

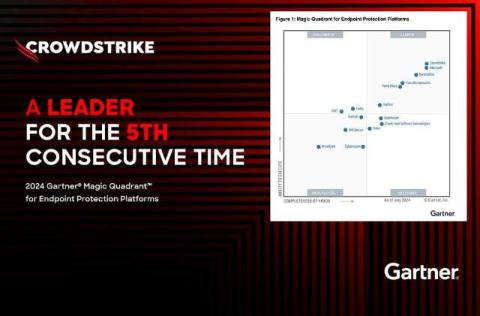
CrowdStrike Named a Leader in 2024 Gartner Magic Quadrant for Endpoint Protection Platforms

CrowdStrike is proud to be named a Leader in the 2024 Gartner Magic Quadrant for Endpoint Protection Platforms. We believe this recognition clearly demonstrates the power of the CrowdStrike Falcon cybersecurity platform and our unwavering commitment to innovation in strengthening endpoint security for our customers.

The 443 Podcast - Episode 307 -How To Deanonymize the TOR Network

This week on the podcast, we discuss how German law enforcement managed to deanonymize and arrest users on the TOR network. After that, we discuss why the US government is trying to ban Chinese-manufactured car hardware. We then end with a cool research article on chaining open redirect and iframe issues into a 1-click vulnerability that grants attackers access to arbitrary Google Docs files. The 443 Security Simplified is a weekly podcast that gets inside the minds of leading white-hat hackers and security researchers, covering the latest cybersecurity headlines and trends.

Zero Trust Models Against Emerging Threats

Cybercriminals have become more sophisticated than ever and have access to many tools to carry out their attacks. It's important to understand that cybersecurity is not a one-and-done task, but rather an ongoing process that requires constant assessment and improvement. This is why the cybersecurity industry is evolving rapidly, embracing new protection methods that integrate AI-powered technologies and services to automatically detect threats and stay one step ahead of advanced attacks.

#153 - Unpacking the hacker mindset with Ken Westin, Senior Solutions Engineer at LimaCharlie

On this episode of The Cybersecurity Defenders Podcast, we unpack the hacker mindset with Ken Westin, Senior Solutions Engineer at LimaCharlie. Ken is a seasoned thought leader in cybersecurity who has spent years analyzing and understanding the intricacies of cyber threats and the methods behind them. Ken has a unique ability to identify emerging trends in the industry and for figuring out how businesses can protect themselves before they fall victim to attacks.

The 443 Podcast - Episode 306 -Kicking EDR Out of the Kernel

This week on the podcast, we discuss Microsoft's recent Windows Endpoint Security Ecosystem Summit and what it means for the future of endpoint security on the Windows platform. After that, we cover a research post on a malware campaign using Google Sheets as a command and control channel before ending with a chat about the US federal government's push to classify cybersecurity as a national service role.