Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

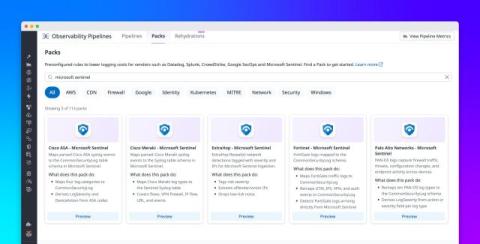
Transform and route security logs to Microsoft Sentinel tables using Observability Pipelines

Microsoft Sentinel is Microsoft’s cloud-native SIEM for detecting, investigating, and responding to threats across your environment. To query security data and run analytics rules, Sentinel expects telemetry data in specific table schemas. But firewall, VPN, and network detection logs arrive in vendor-specific formats, making source-specific mappings difficult to maintain as environments grow.
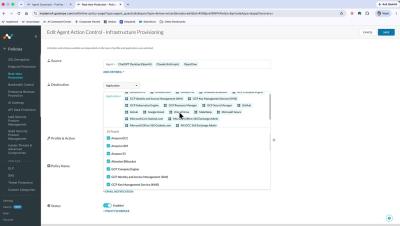
Demo - Agent Action Control

Netskope Skylight Agent Action Control is an inline security capability within the Netskope Skylight AI Security suite designed to evaluate, govern, and enforce real-time controls over the actions performed by autonomous AI agents. Rather than simply blocking or allowing an entire AI application or coding assistant, it intercepts attempted agent operations—such as code pushes, database modifications, or API calls—before they execute.

'Set menu or à la carte?' Customizing the Identity Manager UI

A “set menu” or “à la carte” design? Drawing on nearly 12 years of experience using Identity Manager by One Identity, Andrew Edney, a lead consultant at iC Consult, gives a lightning-quick breakdown of useful UI customization options using Designer, including changes to overview forms and updating navigation with features like custom filtering.

CrowdStrike Accelerates Real-Time Data Classification with On-Device AI

Modern data security depends on understanding sensitive data as it is created, accessed, and moved in real time directly on the endpoint. In addition to identifying predefined patterns such as credit card numbers or Social Security numbers, organizations must protect unstructured information including documents, chat logs, support tickets, AI prompts, medical records, and free-text fields.

More Vulnerabilities Are Being Found Than Ever Before. That's Good News.

If you've glanced at a vulnerability tracker lately, the numbers look alarming. The Forum of Incident Response and Security Teams (FIRST) now projects roughly 66,000 CVEs will be published in 2026; up from a February forecast of 59,427 and closing in on 70,000 by some counts. That would follow a record 2025, which finished at roughly 48,000 disclosed CVEs, itself a sharp climb from about 40,000 the year before. It's tempting to read that curve as a sign that software is getting worse. It isn't.

Best Dark Web Monitoring Services for Business

Most security stacks still find out about stolen credentials the hard way: when an attacker logs in with them. Sometimes the first warning sign is a customer complaint or a call from law enforcement. Dark web monitoring services for business close that gap by watching underground sources for any exposure tied to your domains, employees, code, and brand, so you can reset access before someone else gets there first.

Emerging Threat: (CVE-2026-70756) Oracle WebLogic Server Takeover via T3 and IIOP

CVE-2026-70756 is a vulnerability in the Core component of Oracle WebLogic Server, part of Oracle Fusion Middleware. An unauthenticated attacker with network access over the T3 or IIOP protocols can compromise the server and take full control of it. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical). Oracle rates it as easily exploitable, with no privileges and no user interaction required. Confidentiality, integrity, and availability impacts are all rated high.