Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Turning 1-Star Reviews Into 5-Star Ratings: A Response Playbook

There are 250 million online customer reviews posted across digital platforms every day. But the volume isn't the major issue here. A single unaddressed one-star rating can instantly derail weeks of hard-earned brand momentum. Ignoring these public complaints costs real revenue when prospective buyers look elsewhere. Turning a scathing comment into a positive rating isn't about winning an argument online. It requires immediate action and strategy to transform angry customers into your most devoted brand advocates.
How To Research a Cryptocurrency Before Jumping In

A brand-new token can go from unknown to trending in a single afternoon, and that speed is a big part of crypto's appeal. It's also why jumping in blind can sting. A little homework before you buy won't guarantee a win. It can, however, help you separate promising projects from hype that fizzles out by the weekend.

How to Keep a Game Server Safe From Crashes and Data Loss

Two years of building, gone in one afternoon. It happens to a group somewhere every week. Usually it starts small. A plugin updates badly. The power blinks during a save. Someone types a command they shouldn't. And the world file ends up half-written and unreadable. None of those things are rare. But almost all of them are survivable, if you set things up before they happen. Here's how.

How To Review A Device Photo As Image To 3D

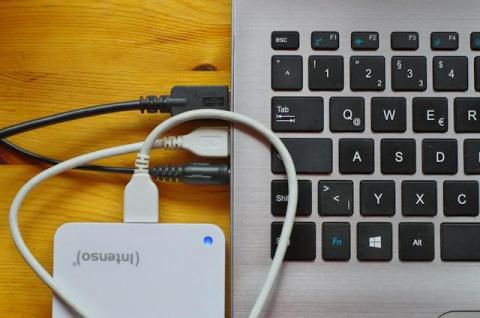
Hardware writeups often have one photograph and a port the photo never turned toward the lens. A reviewer can describe that port from a datasheet, or they can ask a mesh to show the hidden side so a reader can turn it. That second path is what image to 3d is for when the source is a single clear device photo, and it is a starting mesh rather than a measured scan of the board.

What Business Email Compromise Really Costs You

Business email compromise can turn one convincing message into a six-figure loss, days of disruption and a difficult recovery effort. Criminals study how an organization communicates, then impersonate executives or trusted suppliers to redirect legitimate payments. The direct financial loss may be only the beginning. Legal advice, incident response, delayed projects and damaged supplier relationships all raise the final bill. Effective protection therefore depends on coordinated email security, payment controls and verification procedures.

CRA vs NIS2: Does Your Business Need to Comply With Both?

CRA vs NIS2: Which EU cybersecurity regulation applies to your business? Could your company face obligations under the Cyber Resilience Act, NIS2 Directive, or both? If your organisation develops software, manufactures connected products, or operates in a regulated European sector, understanding the difference between CRA and NIS2 is essential for identifying your cybersecurity compliance responsibilities.

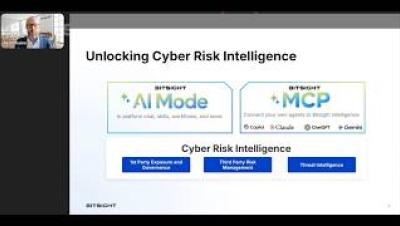
Bitsight MCP and Agentic AI Workflows: A Practical 90-Day Guide

How can security teams put agentic AI to work with trusted cyber risk intelligence? Discover how Bitsight MCP and Bitsight AI Mode help teams investigate cyber exposure, prioritize vulnerabilities, assess third-party risk, and automate security workflows. In this 45-minute webinar, Bitsight experts Christina Chehade and Tadd Hopkins demonstrate practical ways to bring AI into cybersecurity operations, from natural-language investigations to repeatable agentic workflows. You'll also get a 30/60/90-day roadmap for moving from initial exploration to scalable automation.

The Best AI Vendor Risk Management Tools in 2026

Conventional vendor risk tooling asks whether a supplier will suffer a breach. For an AI provider that question is necessary and incomplete, because the larger exposure is what the provider does with your material while operating exactly as intended. ‍ Retention periods, training use, inference location and the model serving an endpoint are data governance questions rather than security ones. Most platforms in this market have no field for them, which is the first thing to check. ‍

Cyber Risk Quantification Vendor Evaluation Checklist

Buying a cyber risk quantification platform means asking a vendor to defend numbers that will end up in front of a board, an auditor, or a regulator. Most evaluation calls never press that hard. The questions below are the ones that separate platforms from each other, and they are written so that any vendor can answer them, including vendors who would beat Kovrr on several of the answers.