Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Beyond Renew or Replatform: A Fourth Option for VMware Customers

A customer tells you they want off VMware. They have seen the headlines, looked at the latest renewal, and decided it is time to evaluate Nutanix, Proxmox, public cloud, or another virtualization platform. The opportunity appears straightforward: help them select an alternative and build the migration plan. But what if leaving VMware isn’t actually the best answer? A platform move is risky, time-consuming, and expensive.
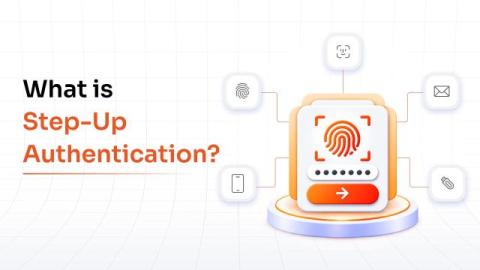
Step-Up Authentication: How It Works, Use Cases and Benefits

A user signs in to an application and gets access to the dashboard. Later, the same user tries to change account settings or approve a high-value transaction. Suddenly, another verification step appears. Why? The risk has changed. Routine access and sensitive actions do not need the same level of protection. Step-up authentication lets organizations add stronger verification when users cross a higher-risk threshold, while keeping everyday access simple.

Who's Behind Your AI Agent? | Teramind AI Usage Control

An AI agent can summarize, classify, and move customer data in seconds. An activity log can tell you what happened, but not why a person set it in motion. Teramind AI Usage Control connects the human action to the AI tool, the data involved, and the behavior that follows, across devices, apps, and workflows. With Teramind, security and IT teams can.

What's taking DNS-PERSIST-01 so long?

In February, Let’s Encrypt announced that DNS-PERSIST-01 was coming, “some time in Q2 2026.” It’s October, and it’s nowhere close to ready. We’ve been waiting for DNS-PERSIST-01 since January, along with every other ACME client and lots of organizations. DNS-PERSIST-01 promised to simplify domain validation and make automation easier, but we had to wait on Let’s Encrypt. Let’s Encrypt is waiting on a redesign, a standards body, and maybe one more vote.

Cyber Loss When the Inventory Itself Perishes

An outage is normally modeled as deferred revenue. Production stops, orders wait, operations resume and some of the backlog is recovered by running longer. ‍ Where the inventory perishes, none of that applies. The stock is destroyed during the incident, restoring the systems does not bring it back, and running longer afterward produces new product rather than recovering the old. ‍

The AI Incident Reporting Duty Nobody Can Date

Compliance content answers the question of when an obligation starts. For the serious incident reporting duty in the AI Act, the honest answer is that it is disputed, and the dispute is not a failure of research. ‍ Two readings of the text point in different directions, neither is obviously wrong, and no authority has resolved it. What follows is the reasoning on both sides and what to do without picking one. ‍