Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

2026 Demo of the Check Point Exposure Management Platform

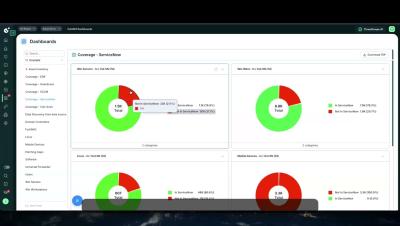
See how Check Point Exposure Management connects external threat intelligence with what is exposed inside your environment, so your security team knows which threats matter and what to fix first. In this 14-minute walkthrough, Check Point Software shows how Check Point Exposure Management turns 15 years of threat intelligence collection, covering the deep and dark web and threat capture monitoring, into prioritized, actionable exposure data. You see which threat actors and campaigns are relevant to your organization, which vulnerable hosts they could reach, and how to block them in real time.
CAASM and Vulnerability Prioritization Demo: See the Full Picture Across Your Security Tools

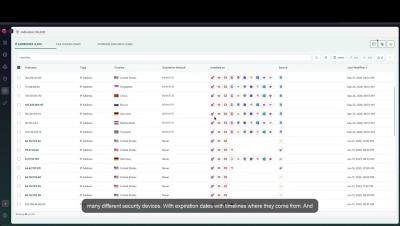
No single security tool shows the full picture. See how Check Point Exposure Management pulls findings from dozens of tools into one view, so your team can see which assets are exposed, which controls are missing, and what to fix first.

Check Point Exposure Management Safe Remediation Demo: Harden Firewalls, Endpoints Operating Systems

Closing an exposure should not cause an outage. See how Safe Remediation in Check Point Exposure Management turns findings into validated fixes on the security controls you already own, without business disruption.

Zenity Launches Universal Runtime Control for Claude Enterprise

Anthropic's Inference Hooks update lets security teams validate Claude's tool calls before they run. Zenity supports it across Claude's surfaces, so teams can approve write-capable connectors, Model Context Protocol (MCP) servers, and wider Claude Code rollouts with policy on each action.

Architecting Trust: The Data Pipelines and Infrastructure Behind The Guardian Agents

As AI agents operate with increasing autonomy in enterprise production, the sheer volume of security telemetry they generate creates an unprecedented scaling challenge. Human oversight remains required in many enterprises, while legacy triage tools simply can't keep up. To help security teams cut through the noise, Zenity’s AI group built the Blue Agent.

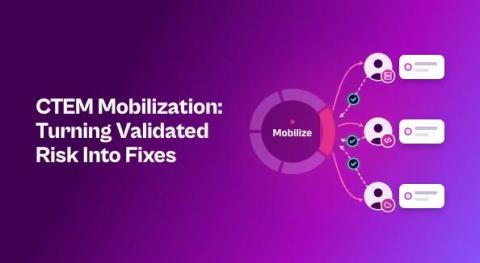
CTEM Mobilization: Turning Validated Risk Into Fixes

Mobilization is the fifth and final stage of continuous threat exposure management (CTEM). It turns validated, prioritized exposures into action by assigning clear owners, delivering context-rich work into the tools teams already use, choosing the fastest safe response, tracking SLAs, and verifying that fixes worked. It’s often the hardest stage because security teams find exposures but IT, engineering, and cloud teams fix them.

Between a Rock and a Hard Place: When Dependency Cooldowns and CVE Policies Deadlock the Build

On a recent call, a security lead walked us through two rules his team enforces on every build. Both are sensible. Together, they left his developers with a red pipeline and no version of a library they were allowed to use. The first rule is a cooldown. A new open source release cannot enter the build until it has been public for a set number of days. The second rule blocks any library version with a known high or critical vulnerability.