Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What's New With Keeper | February 2026

The Keeper Security Government Cloud (KSGC) platform has been authorized at the FedRAMP High baseline, enabling federal civilian agencies to protect high-impact unclassified data as defined under FIPS 199 and FedRAMP High baselines. The “High Impact” designation applies to systems where unauthorized access or disruption could cause severe or catastrophic harm to agency operations, assets or individuals.

AI Principles in Practice: Auditability in non-negotiable

When AI acts on your behalf, auditability is non-negotiable. In the latest Principles in Practice video, Anand Srinivas, 1Password VP of Product & AI, explains why every AI agent action involving credentials must leave a clear audit trail: Who approved the access and why When and where were credentials used What did the agent access and when Did access end when the task was completed Without auditability, AI usage can break trust between employees, security teams, customers, and regulators.

Anomaly Detection with Machine Learning to Improve Security

Being a security analyst can feel like being trapped in a Where’s Waldo book. You can find yourself staring at a data stream looking for something that “isn’t like the others.” However, as your organization collects and correlates more data from the environment, finding the Waldo can feel overwhelming. In a modern IT environment, organizations have hundreds or thousands of devices, users, and data points that they need to correlate so they can identify normal network activity.

Passing SOC 2 Without the Overhead: How Zero Standing Privileges Simplifies Compliance

Getting ready for a SOC 2 audit can feel like an endless checklist. You already have tools collecting logs, provisioning users, and pulling reports from your systems, yet proving compliance still feels harder than it should be. The biggest pain in SOC 2 is not collecting data. It is managing access in a way that continuously aligns with your own policies.

Why You Can No Longer Trust What You See

Deepfakes and AI driven attacks are making it hard even for experts to tell what is genuine, from casual social videos to targeted messages. Recent cases used convincing voice and chat to pressure staff into password resets, fund transfers and access changes, forcing organisations to rethink how people validate what they see and hear.

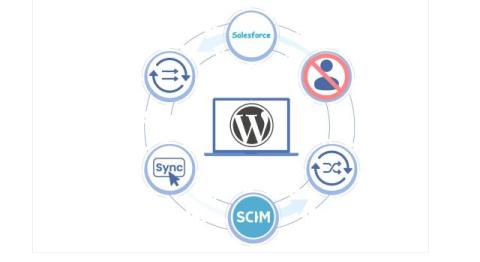
User Provisioning and Data Synchronization - User Synchronization for WordPress

With the growth of any business or organization, the importance of data accuracy, consistency, and privacy is rising. Things that may seem like a minor data error or glitch can have a major negative impact on sales, decision-making, and customer retention.

AWS ECR Scanning: The Practical Guide to Securing Your Containers

If you operate containers on AWS you’re likely familiar with how vulnerabilities can accumulate. The majority of container images currently include least one critical security flaw. Frequently hidden within a base image or an overlooked dependency. This makes enhancing your AWS container security essential. It’s the method to prevent problems such, as data leaks, privilege abuse and supply-chain threats.