Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

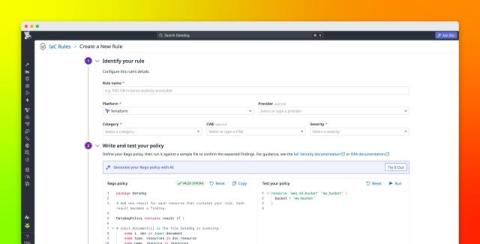
Enforce custom rules in Datadog IaC Security scanning

Infrastructure-as-code (IaC) security scanning can catch common misconfigurations before deployment, but every organization also has internal requirements that a default rule catalog cannot cover. For example, teams may need to enforce required tags, approved instance types, or naming conventions. With custom rules for Datadog IaC Security, security and platform teams can define these requirements as Rego policies and run them alongside Datadog’s default rules during IaC scans.

PQC Post Quantum Cryptography Explained: Why Today's Encryption Has an Expiration Date

The encryption protecting today’s data isn’t broken, but it does have a timeline. This video breaks down why current systems like TLS, PKI, and RSA remain secure today, and how quantum computing will change that. As progress accelerates toward large-scale quantum machines, organizations must prepare for a new era of security. Learn how PQC (post-quantum cryptography) helps address emerging risks like “harvest now, decrypt later,” and why tracking adoption of quantum-safe encryption is critical now, not later.

CVSS Scores Alone Can Mislead Vulnerability Prioritization

Not every high-severity vulnerability represents the highest risk. Learn why effective prioritization requires more than a CVSS score and how factors such as reachability, exploitability, active exploitation, and asset criticality provide the context needed to focus remediation efforts where they matter most.

Cineworld Glitch Purportedly Allows Users To See Member Card Details

On 17 September 2026, users on X (formerly Twitter) posted that payment details belonging to other individuals had appeared on the Cineworld app under their personal accounts. On 17 September 2026, users on X (formerly Twitter) posted that payment details belonging to other individuals had appeared on the Cineworld app under their personal accounts.

CVE-2026-67401: SQL Injection in cPanel's EmailTrack Puts Shared Hosting Environments at Risk

A critical SQL injection vulnerability has been identified in cPanel & WHM’s EmailTrack functionality. The vulnerability was disclosed by cPanel on September 8, 2026, affecting every supported release line. It allows an authenticated cPanel account holder with mail related privileges to ultimately achieve root-level code execution on the underlying host.

What is SLH-DSA? Hash-Based Post-Quantum Digital Signature Guide

SLH-DSA is NIST’s standardised post-quantum digital signature algorithm (hash-based). It generates quantum-resistant signatures, ensuring signatures are not changeable and that they will not be forged, even when later superseded by schemes like RSA and ECDSA, which are susceptible to attacks by quantum computers. Organisations are studying it today because large-scale quantum computers could, in the future, crack the algorithms that currently underpin most digital trust.

How Public VIN Records Become Part of Your Digital Footprint

When people think about online privacy, they usually consider email addresses, phone numbers, social media accounts, or browsing activity. Vehicle information rarely comes to mind. Yet a car can develop its own extensive digital footprint. A Vehicle Identification Number may connect publicly accessible auction listings, photographs, mileage readings, damage descriptions, specifications, and sale information that remain searchable long after the original event.

Agentic AI for ITOps: Is your organization ready for the security challenges?

AI is set to provide increasing value in IT by enabling more ways to simplify complex IT operations, offering actionable insights, automating routine tasks with context-aware automation, and detecting abnormal events with advanced machine learning algorithms. With agentic AI, systems can understand what is happening in an IT environment, reason about the most probable root causes, determine the right course of action, and implement these changes without requiring additional human intervention.

What OpenAI's Misalignment Reports Tell Security Teams About AI Agents

AI Agents are no longer the new insider threat. They’ve become firmly planted as the primary challenge for security leaders when it comes to insider threat activity. They have credentials, they act autonomously, and increasingly, they can take real actions on real systems. How would you know when one of your digital workers starts doing something it’s never done before?