Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Known Exploited Means Your Mitigation Is Next

Last month, the FBI arrested a suspect in its ongoing response to an attack on its job portal, allegedly carried out by criminal hacker and extortion group ShinyHunters. The agency said a contractor failed to apply a security patch to a third-party platform involved in the breach of its job portal, while Reuters reported that the contractor worked for Accenture and that the platform was Oracle PeopleSoft. (Fair warning: The Reuters article is behind a paywall.)
AI-accelerated Vulnerability Discovery Demands Rethinking Vulnerability Management Practices

Enterprise security has a speed problem. Attackers are getting faster at finding and exploiting vulnerabilities, while many organizations still rely on ticket-based remediation, approvals, and scheduled maintenance windows. AI threatens to widen that gap considerably, exposing one of vulnerability management’s largest unchanged challenges: getting the right systems to fix the right problems before attackers exploit them.

PHP2Shell Critical RCE Flaws: Exploited Within Hours of Disclosure

Last updated: October 22, 2026. This story is still developing, and we'll update this post as new details are confirmed. Two critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619, are putting a large share of the web at risk. The vulnerabilities, collectively named PHP2Shell, both carry a CVSS score of 9.2, and both allow remote code execution (RCE). Security teams should treat these vulnerabilities urgently and respond accordingly.

There's Something Missing in the Discussion About AI in Vulnerability Management

The platform determines what is known. AI helps determine what it means. Technology solution providers across virtually every industry are racing to add AI, in some fashion, to their offerings. Vulnerability management providers aren’t immune, either. They’re racing just as fast as the rest of them, sometimes faster. These vendors are embedding copilots, assistants, and agents powered by technologies like Anthropic Claude, OpenAI GPT, and Google Gemini.

Risk Acceptance Has a Shelf Life: Notes from the Aviation ISAC Cybersecurity Summit

The first Aviation ISAC summit, a little over a decade ago, was about forty people in a room in Miami, hosted by the Health ISAC. This year’s conference in Vancouver hosted more than five hundred: airlines, airports, OEMs, suppliers, and government, all in one place for three days. Many in the audience were new to the conference. One of the opening speakers asked first-timers to raise their hands, and a lot of hands went up around the room.

FBI Winter SHIELD's Cybersecurity Controls Are Worth a Second Look

AI adoption is making everyone faster, including the attackers we as cybersecurity practitioners are competing with. While the attackers are getting faster thanks to AI, it’s not changing why most preventable breaches happen. That part is remaining consistent, for better or worse.

Automate Vulnerability Reporting for Auditors Without Creating More Work

Anyone who has participated in a cybersecurity audit knows the drill and has likely asked the same question. “Is there a way to automate any of this?” When an auditor requests evidence that vulnerabilities are being identified, prioritized, remediated, and tracked according to policy, the automation question is a fair one.

How AI Changes Exposure Management: From Static Findings to Continuous Risk Decisions

Every security team knows the feeling. The quarterly vulnerability scan completes. The report lands, with thousands of findings, color-coded by CVSS severity, neatly timestamped. And the moment it’s printed, it’s already out of date. That is the fundamental flaw at the heart of traditional exposure management: it is built around a point in time.

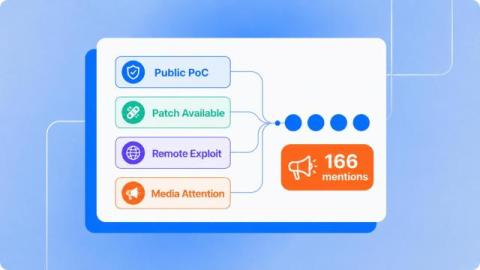
Exploitability Without Exploitation: When Attention Is the Signal

Nucleus Insights flagged 14 vulnerabilities with real-world exploitation activity that looked risky before CISA added them to KEV. The key takeaway: all 14 were later listed in KEV. Acting on those signals would have been the right call every time, just earlier.

Nucleus Helix Was Built to Fix Exposure Management's Breaking Point

Let me be direct about something the industry keeps dancing around: the vulnerability problem isn’t getting better. It’s getting structurally worse. The wave of AI-generated code and compression of time to exploit thanks to frontier AI models like Mythos is about to make “worse” look quaint. If your vulnerability and exposure management program is still built around scanner cycles, ticket queues, and CVSS scores, you’re not running a security program.