Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Are vulnerability scan reports dangerous?

Vulnerability scan reports are requested from a wide variety of people or entities for many different reasons. Historically a report meant a static snapshot of the scan data. Some company stakeholders may want an executive overview of the current vulnerabilities present in their environment. In contrast, others may want additional data points such as trending to reflect how well they have made progress in remediating previous vulnerability scans detected.
Threat Intelligence Management - the Foundational Use Case for a TIP

I previously talked about how to get started with a threat intelligence program, which is the cornerstone to any security operation. Such a program enables security teams to gain a deeper understanding of adversaries and their tactics, techniques and procedures (TTPs), in order to determine what is relevant to the organization and how to mitigate risk.

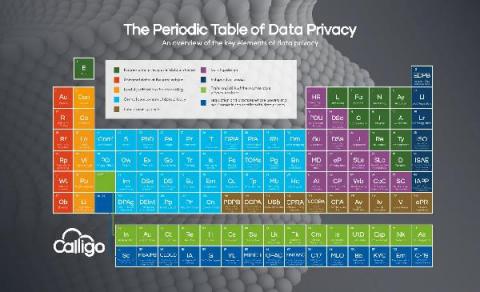
UPDATE 7: The Data Privacy Periodic Table

Since our last update in January, there has been an unprecedented amount of activity in the data privacy world. And yes, we probably do say that every time! New laws have passed in Virginia and Colorado. The UK’s post-Brexit EU adequacy was confirmed. Plus of course, the EU’s significant changes to Standard Contractual Clauses and the reawakening of the debates over Identity Verification, especially in the context of social media.

Tech needs women: an interview with the women leading Fastmail

As we discovered in our Women in Tech panel earlier this year, it’s important to show women succeeding in male-dominated industries, like technology/security, and to talk about how men can help create space for others in the workplace. We’ve previously highlighted our women-led Security team and now want to continue sharing stories about women in leadership by introducing you to two leaders that are helping create space for women and non-binary people in the tech industry.

Spectra Alliance Helps Enable Zero Trust

Zero Trust is not something you purchase. Zero Trust is a security strategy you build out using the working assumption that there are no safe network zones, no perimeters, no safe users, and no safe devices. The Spectra Alliance helps enable a Zero Trust model across the scope of six elements including applications, data, networks, infrastructure, identities, and devices.

White House Memo Takes on Securing Critical Infrastructure Control Systems

Attacks targeting critical infrastructure have been on the rise in recent years. Back in 2019, for instance, 56% of utility professionals responsible for overseeing risk in their organizations’ operational technology (OT) assets told Siemens and the Ponemon Institute that they experience at least one shutdown or operational data loss event a year.

Limitless XDR defined: Ingest, retain, and analyze security data freely

Elastic Security's newest features define the potential of XDR for cybersecurity teams. Our single platform brings together SIEM and endpoint security, allowing users to ingest and retain large volumes of data from diverse sources, store and search data for longer, and augment threat hunting with detections and machine learning. Security vendors are using the term “XDR” with increasing frequency, applying varied definitions to suit their respective technologies.