Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How long does it take to replace every certificate after a CA distrust?

Last week we moved every certificate in one of our products to a new CA in 10 minutes. It was six certificates and 18 deployments. I said issuance was the part that slows down, because most CAs limit how fast you can order, and then I waved it off. A reader did the math for me. Some organizations run 30,000 certificates, they claimed, and that’s common at MSPs, telcos, and government agencies. Google Trust Services takes 100 orders an hour by default.

How Layered Cybersecurity Stops Ransomware and Data Breaches in Mid-Sized Businesses

A layered cybersecurity strategy protects mid-sized businesses by building multiple overlapping defenses, ensuring that if hackers breach one layer, another stops them before data is stolen or encrypted. Single-point solutions fail against modern cyber extortion, leaving growing organizations severely vulnerable. Today, threat actors aggressively target smaller companies that lack enterprise-grade defenses. In fact, an alarming 88% of SMB breaches involve ransomware, making small businesses more than twice as likely to face an attack compared to large enterprises.

School Event Rentals: Safety Compliance Guide for Athletic Directors

Picture a fall Friday evening: students, parents, and staff gather on the athletic field for a school carnival. As the athletic director, you're not just overseeing the scoreboard-you're responsible for ensuring every rented bounce house, obstacle course, and game booth meets safety standards. The challenge lies in balancing the festive atmosphere with strict compliance, so no one is left asking tough questions after an incident.

How Google Ads Services Are Quietly Filling Dental Appointment Books

Many dental practices do not need more website traffic. They need more booked patients. That is where Google Ads services can make a quiet but real difference. This online advertising platform puts your clinic in front of people searching right now, which is why so many practices use it to turn online interest into steady appointment demand.

Threat Advisory - ClickHouse CVE-2026-116366: Unauthenticated Remote Code Execution

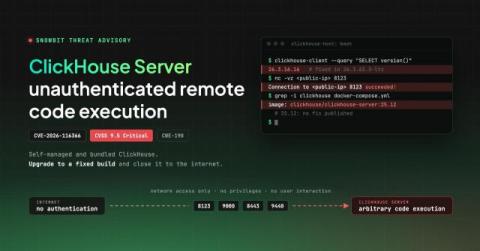
On 30 October 2026, ClickHouse disclosed CVE-2026-116366, a critical vulnerability in ClickHouse Server (CVSS v4.0 9.5). Under certain conditions, an unauthenticated attacker with network access to the server can execute arbitrary code. Third-party vulnerability trackers classify it as an integer overflow (CWE-190); ClickHouse has not confirmed this.

When Geopolitics Hits Your Balance Sheet: What Binance's $6.3B Hack Means for CTOs

Binance never chose to be on the front line of a geopolitical conflict, yet if blockchain-intelligence firms are right, that is where it ended up, and its balance sheet absorbed the first loss. Binance’s initial investigation indicates that a compromised DevOps engineer’s laptop may have given an attacker access to a service container and the ability to submit unauthorised withdrawals.

PCI Compliance Logging: Complete Guide to Requirement 10

Of the 12 Payment Card Industry Data Security Standard (PCI DSS) requirements, Requirement 10 is one your platform team can engineer directly. Under the PCI DSS v4.0.1 standard, automated log review has been a tested requirement since March 31, 2025. Your assessor will test the mechanism that performs the review. This PCI compliance logging guide covers each 10.x sub-requirement, maps the seven event classes to log sources, and lays out a nine-step program you can hand to your assessor.