Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

One Feed, Many Clients: Running Multi-Tenant Threat Intelligence as an MSSP in 2027

his blog explains what multi-tenant threat intelligence is and why running one intelligence feed across many clients is one of the hardest jobs an MSSP has. It covers how a single compromise can spread across a client base, what MSSPs should look for in intelligence built for many tenants, and how the Cyber Security and Resilience Bill raises the stakes for UK providers.
Grandoreiro Malware: An Evolving Threat to Banking Customers

Grandoreiro is a malware family classified as a backdoor and spyware, first seen in April 2020, and is consistently described as a banking trojan focused on credential theft, remote fraud enablement, and control of compromised Windows systems. It has remained active through recurring campaigns, including a renewed wave in May and June 2026 that concentrated heavily on Latin America, especially Mexico, while also reaching parts of Europe and North America.

PHP2Shell and the end of the once-a-year pen test

On October 21, 2026, PHP shipped emergency fixes for two flaws that let anyone on the internet run code on a PHP web server, with no login. The weakness behind them had been flagged in 2024 and then sat, partly because nobody had proved it was exploitable. In 2026, researchers working with AI models proved it within days. Exploit attempts started before the fix shipped, and details leaked a day ahead of schedule. That sequence is the real story of PHP2Shell. The bug matters, but speed matters more.

Cybersecurity for Defence Networks: Protecting Critical Military Information and Systems

Digital technology plays an essential role in modern military operations. Defence organisations use interconnected systems to manage communications, exchange intelligence, coordinate personnel, and maintain operational readiness. However, increased connectivity also creates opportunities for cybercriminals and hostile actors to target sensitive information and critical infrastructure.

What Is TOTP? Security, Implementation, and Best Practices

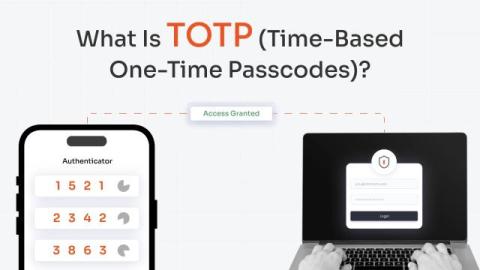
TOTP (Time-Based One-Time Password) is an authentication algorithm that generates a unique, temporary numeric code using the current time as a moving factor. Typically, these codes are six digits long and automatically change every 30 seconds, providing a one-time verification code for authentication. TOTP uses a shared secret between the authentication service and the user's authenticator device, combining that secret with the current time to generate each code.

What is OAuth (Open Authorization)?

OAuth (Open Authorization) is an open-standard authorization framework that allows applications to access an end user's protected resources without requiring the user to share their password. Instead, users grant applications limited access to specific resources through authorization, while their credentials remain private. OAuth uses access tokens to control what an application can access on a user's behalf.

HTTP2Shell: Find and Fix Vulnerable Brotli Copies with Tanium

If you run Node.js, update to 26.12.1, 24.22.1 or 22.23.4 now. If you run Python, upgrade the Brotli package to 1.2.1 and brotlicffi to 1.2.1.0. If you run Bun, move to 1.4.4. All three carry a fix for CVE-2026-111497, an out-of-bounds write in Google's Brotli decoder that can let a remote, unauthenticated attacker crash a process, read its memory or potentially run code by sending it crafted compressed data. Google's CVE record scores it 9.2 under CVSS v4.0.

eMudhra CA Compromise: Find and Fix Your Exposure with Tanium

On October 17, 2026, a researcher reported that eight intermediate certificate authorities (CAs) run by eMudhra have private keys that anyone can calculate from the public certificates. Six of the CAs are for TLS (website) certificates and two are for code signing. Sectigo cross-signed the same eight keys, so 16 certificates are affected in total With these keys, anyone can issue a certificate for any website, or sign software, and it chains to root CAs that many systems trust.

Home Security Mistakes That Can Put Your Property at Risk

Keeping a home secure involves more than installing strong locks or purchasing a security camera. Many vulnerabilities develop through everyday habits, overlooked maintenance, and decisions made when renovating or improving a property. Even homeowners who invest in modern security technology can leave certain areas exposed without realizing it.