Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Featured Post

Cyber Risk and Incident Response: A Growing Priority Across Industries

Cyber risk has become a dominant priority for organisations across nearly every sector. As the severity and velocity of the threat landscape and technological change continue to accelerate, organisations are under increasing pressure to ensure they can keep pace and recover quickly in the aftermath of a cyber event. A core focus for many organisations is strengthening their incident response capability: how effectively the business can react and recover when an attack occurs.

9,000+ Incident Response Investigations Later: The 11 Essential Cybersecurity Controls

Organizations with mature security programs still get breached. Teams that pass audits still find themselves responding to ransomware, Business Email Compromise (BEC), and credential theft. The controls that satisfy an audit requirement and the controls that significantly reduce the likelihood, impact, and cost of an intrusion are often not the same.

Response Options Combats "Patch or Wait" in the Age of Frontier AI

When a vulnerability is urgent but the full fix isn’t immediately safe to deploy, security teams need another way to reduce risk fast. Seemplicity’s Response Options uses AI to identify and rank multiple ways to neutralize a threat – including patches, configuration changes, compensating controls, and network-level mitigations — based on risk reduction, effort, and operational impact.

Response Options: Multiple Methods to Mitigate Risk

Seemplicity’s new Response Options feature gives teams multiple ways to respond to a confirmed finding, not just a single full-fix recommendation. AI Analysts surface and rank fix, neutralization, and mitigation paths based on security impact, deployment risk, and effort, helping teams reduce exposure faster while making safer, more informed remediation decisions. Every exposure management program eventually hits the same wall.

Agent Incident Response: Containment Is the Easy Part

Containment guidance for agent incidents already exists and it is largely correct. Revoke the tokens, freeze the orchestration tier, cut egress, set the vector store to read-only. Those steps take minutes and any competent team will find them. ‍ The difficulty sits either side of containment. Deciding what kind of incident this is takes longer than stopping it, establishing what the agent did before you stopped it takes longer still, and both depend on preparation that has to exist beforehand.

Steps to Recover from Ransomware Attacks Efficiently

A ransomware attack can stop business operations in a very short time. Files may become locked, systems may go offline, and employees may lose access to important tools. In some cases, attackers may also steal data before blocking access to it. Recovering from ransomware takes more than simply restarting computers. Businesses need a clear plan for containment, investigation, data recovery, system repair, and future protection. A rushed response may make the damage worse or allow attackers to return.

How to Improve MTTR: A Practical Guide for Security Teams

A critical alert enters the SOC queue during the overnight shift. By morning, the dashboard shows an acceptable headline MTTR because the incident was closed quickly after an analyst finally picked it up. The timeline tells a different story: the alert sat unassigned for nine hours because severity routing sent it to the wrong queue. The team optimized the visible number while leaving the dangerous delay untouched.

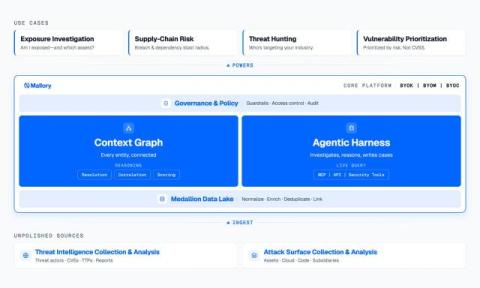
Mallory Unifies Threat Intelligence, Exposure Context, and Response Into One Architecture for Security Teams

As AI-assisted attackers compress exploitation timelines to hours, Mallory turns live adversary intelligence into prioritized, policy-governed action across the tools security teams already run.