Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

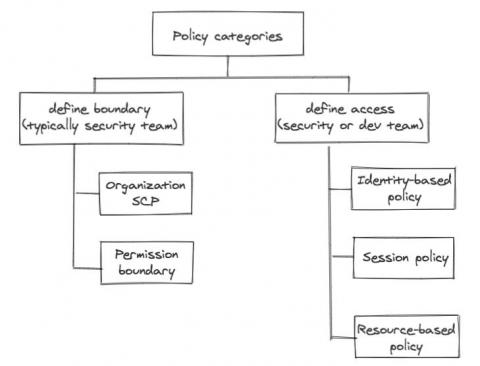
AWS IAM in a layman's terms

We alluded in one of our previous posts that the development team will own a lot of responsibility defining application related resource access control, simply because the dev team owns the infrastructure as code (IaC) responsibility themselves. No matter how security-savvy and security-educated a development team is, the central security team still needs some control, some kind of “trust but verify”.
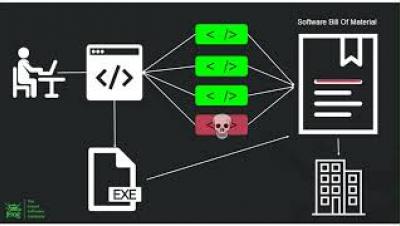
Joe Biden's Security Order: What it Means for DevOps

What the Executive Order says today Anticipated further actions by the White House Reasons the software bill of materials (SBOM) will become the source of truth Differences between a SBOM and an “ingredients list” How tools and methods will position developers for success How securing and certifying processes - not just components - may be the key to future compliance

Advancing SBOM standards: Snyk and SPDX

Many people will have heard of the SPDX project through the work on the SPDX License List. This list of canonical identifiers for various software licenses is used in a huge range of developer-focused software, from Snyk to GitHub. But the SPDX project, which is part of the Linux Foundation, has a much broader focus on providing an open standard for communicating software bill of material information.

Snyk provides native integration for Atlassian Bitbucket Cloud security

We’re excited to share that we have enhanced our partnership with Atlassian. In support of this partnership, today we are releasing full availability of the new integration, which natively embeds Snyk into Bitbucket Cloud for security. The Snyk security integration is free and easy to set up with just a few clicks inside the Bitbucket Cloud product. For the first time, developers can consume information that was previously only available inside Snyk now within Bitbucket Cloud.

Research Shows Over 100,000 Libraries Affected By Maven Vulnerability CVE-2021-26291

By Jonathan Leitschuh; Daniel Elkabes, Senior Security Researcher at WhiteSource; Ofir Keinan, Software Developer at WhiteSource The latest Maven release 3.8.1 contains a fix to security vulnerability CVE-2021-26291. Detected and reported by security researcher Jonathan Leitschuh, the vulnerability affects over 100,000 libraries in Maven Central, according to the WhiteSource security research and knowledge teams.

Get Kubernetes Backup - CloudCasa - in 1-Click from DigitalOcean Marketplace

Are you a DigitalOcean vendor or user and developing or deploying a Kubernetes application? You may want to preserve your cluster configuration, backup your persistent volumes to protect them from ransomware, accidental deletion, and long-term retention policies. CloudCasa is the only data protection and disaster recovery solution that has been tested and certified as a 1-Click appliction with DigitalOcean Kubernetes and available in their marketplace.

ServiceNow Incident using NLP Insights | Robotic Data Automation (RDA) | Tejo Prayaga | CloudFabrix

Robotic Data Automation (RDA) helps enterprises realize value from data faster by simplifying and automating repetitive data integration, preparation and transformation activities using Low-Code workflows and data bots, including built-in AI/ML-bots.

Easily map Snyk vulnerabilities to Cortex services

Snyk is a developer-first, cloud native security platform that scans for vulnerabilities across code, dependencies, containers, and infrastructure as code. Snyk does a great job of surfacing vulnerabilities in your codebase, but it can often be challenging to map these issues back to actual services and their owners. Fortunately, Snyk’s robust API can be used to tune Snyk to integrate into solutions designed to help engineering teams understand and improve their service-oriented architecture.

10 Supply Chain Security Tips That Won't Slow Development Down

As supply chain attacks continue to dominate headlines, software development teams are beginning to realize that package management can’t be taken lightly — the threats hidden under the hood are real. In this installment of The Source, we want to talk about the practices and tools that developers need to adopt in order to protect against supply chain attacks.

Understanding the software supply chain security requirements in the cybersecurity Executive Order

President Biden’s cybersecurity executive order from last month should cause little surprise for anyone following news headlines over the past year. The order is the U.S. Federal Government’s important response to a long list of incidents, starting with the SolarWinds attack and ending with a recent ransomware attack against Colonial Pipeline —- the largest known attack against a US energy firm.