Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Data Security including privacy, protection, and encryption.

Where Does Session Replay Cross the Line?

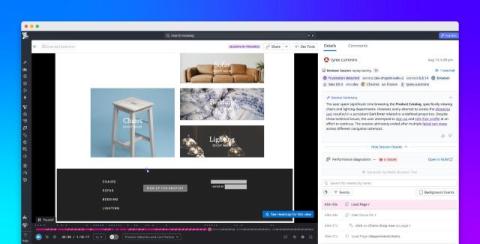
Session replay has quietly become default infrastructure. Product teams want to see where users stall, support wants to stop asking "can you send a screenshot," and engineering wants a reproduction path for the bug that only happens on one customer's machine. The business case writes itself. The security review, in most organisations, never really happened. So when the question finally comes up - where does this stop being lawful? - most teams go looking for the answer in the wrong place.

Best Unified Data Security Platforms for 2026: 7 Compared

Security teams comparing unified data security platforms in 2026 are no longer just choosing between DLP vendors. They're deciding how much of their data security architecture, discovery, classification, enforcement, insider risk, and AI governance should live in one system versus remain assembled and operated from separate tools. That decision has gotten harder. DSPM vendors are adding DLP. DLP vendors are adding posture management. Everyone claims AI coverage.

SACR's New ECP Framework: What It Means for AI and Data Security

A new report from Software Analyst Cyber Research (SACR), The CISO Guide to Endpoint Control and Prevention (ECP): The Next Architecture for Endpoint Security, outlines a new era of endpoint security shaped by AI agents, copilots, SaaS applications, browser-based workflows, and increasingly autonomous activity. The report introduces Endpoint Control and Prevention (ECP) as a framework for understanding this shift and the new security capabilities it requires.

How to Protect Digital Ministries in the Age of Cloud Computing

Church ministry no longer stops at the sanctuary door. Livestreams, online giving, prayer forms, volunteer platforms, email systems, and social channels now carry much of the weekly work. That reach is certainly important. But still, every new account creates another place where credentials, personal records, or payment information can slip into the wrong hands. Churches often manage this digital estate with small teams, rotating volunteers, and limited technical oversight.

Cloud Computing Security for Community Organizations: Protecting Sensitive Data

Church work today runs through shared drives, livestreaming platforms, donation portals, email accounts, volunteer databases, and pastoral care systems. That shift happened gradually, often without a formal security plan. One tool arrived for scheduling, and another handled giving. At the same time, someone created a spreadsheet for member details. Before long, sensitive information sat across several cloud services, managed by staff and volunteers with very different technical skills.

Reduce sensitive data exposure with build-time allowlists

Build-time allowlists help teams preserve readable Real User Monitoring (RUM) action names while reducing the risk of exposing runtime-generated sensitive data. RUM action names turn user interactions into descriptions that engineers can use to understand application behavior, but that readability can also create risk. Datadog provides a build-time privacy approach that preserves readable action names when their contents are known to be static while masking text constructed at runtime.

When Reading Apps Handle Sensitive Documents: A Practical Privacy Checklist

Read-aloud and AI explanation tools can make difficult material easier to use. Before opening a confidential PDF, however, users should understand where the text goes, what the app stores and which permissions it really needs.

Best practices for audit trails and file tracking in secure data exchanges

Audit trails and file tracking are essential for ensuring accountability and transparency in sensitive data exchanges. Regulatory demands make robust traceability especially crucial as expectations for breach investigation and third-party oversight grow. This article explores how effective monitoring can help organizations meet security challenges and maintain compliance.

4 Easy Standards To Protect Team Data

Protecting team data starts at the workstation level, moving beyond access logs or password policies to secure the physical environment each employee operates in every day. Inconsistency creates immediate exposure points across the office because varying screen habits and device positions generate discrete gaps that software policies cannot close alone.