Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

4 Best Practices to Guarantee Successful AWS Migration

Successful AWS migration takes more than simply choosing to migrate. It’s a journey, and you need to be confident in your choice to upend your existing on-premise workflows to align with your business’s future. The fundamental process around a migration strategy includes understanding the benefits of a new system, assessing gaps in your existing system, migration planning, and ultimately the actual migration aspect.
NIST Cloud Security: Standards, Best Practices, & Benefits

Latest cloud security statistics reveal that 91% of all organizations have some portion of their IT environment hosted in cloud platforms. While cloud computing comes with many benefits, companies have trouble scaling up the security to meet the data and privacy challenges posed by it.

Making Content Security Policies (CSPs) easy with Page Shield

Modern web applications are complex, often loading JavaScript libraries from tens of different sources and submitting data to just as many. This leads to a vast attack surface area and many attack types that hackers may leverage to target the user browser directly. Magecart, a category of supply chain attack, is a good example.

Best in Class

Why AWS indeed. This is not one of those start with why posts, but hopefully a peek into the reasons behind our partnership with AWS and what that means for you and how it could benefit you. The beginnings of something great Public cloud is well established, with about 50% of all workloads now running in a public cloud location. We have heard of ”the big three” cloud providers: AWS, Azure, and Google Cloud.

Easily Enable Encryption: Secure Cloud-native Development Series

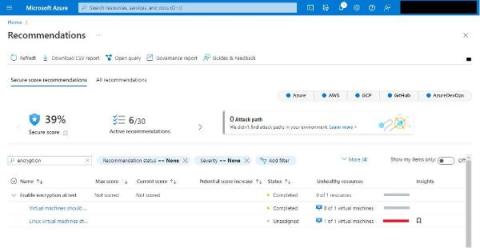
Build secure cloud-native applications by avoiding the top five security pitfalls we lay out in our Secure Cloud-native Development Series. This blog is the fourth part of the series, and it will teach you why and how to easily enable encryption and save yourself headaches down the road. Here's a new motto: encrypt everything! When securely moving to cloud-native technologies, building encryption in from the start will save us a lot of headaches later.

How To Write A Post-Audit Cloud Security Report

A post-audit cloud security report is a document that provides an overview of the security status of the cloud environment, infrastructure, and applications of a business. It verifies that vulnerabilities and security flaws have been identified and assessed, and offers recommendations to address these security gaps.

How To Conduct An Azure Security Audit: The Actionable Guide

Over 56% of organizations globally use Microsoft Azure for their cloud services owing to its convenience, cost-effectiveness, and scalability. It is vital to secure your Azure environment against the backdrop of an ever-evolving threat landscape. Otherwise, your database and digital assets can leak sensitive data. And one way to do it is through Azure security audits.