Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Create an API Specification Scan

Traditionally Veracode Dynamic Analysis has targeted applications with a Web user interface. But increasingly, web applications are composed of many small microservices, many of which have Representational State Transfer (REST) interfaces with which the UI layer communicates. With API scanning, you can now scan the APIs of your microservices earlier in the software development process, before they are integrated into a web application.
A Proof-of-Concept for API Caching at Egnyte

As Egnyte’s business and customer base grows, we have an engineering responsibility to provide data quickly and at high availability. In this blog I’ll recap one of those efforts—a proof-of-concept API caching project that serves our large folder listing capabilities and has future applications in other Egnyte services.

Snyk's shift left approach to API development

Snyk’s developer security platform provides developers and security professionals with the tools they need to build and operate modern applications securely. Snyk enables users to shift security left and to embrace a DevSecOps model. Modern application development teams understand that shifting left means bringing information to developers’ fingertips as early as possible in the development process to create efficient and secure applications and development processes.

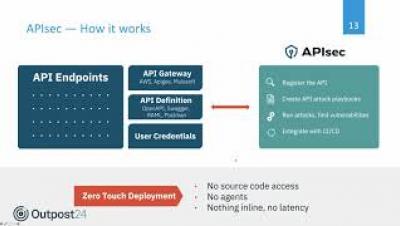
Outpost24 Webinar - API security 101 and how to secure your web applications

APIs are a key part of modern web applications and a growing security challenge that isn’t well understood by developers and application security managers, leading to exposed APIs that give hackers access to sensitive data. Find out how to secure your APIs and prevent vulnerabilities from making it into production.

Tooling Overview for API Testing (SAST, DAST, IAST, Fuzzing)

Application Programming Interface (APIs), allow services to communicate with each other. Naturally, applications that are interconnected through many APIs, require thorough security testing, as each connection could potentially include software vulnerabilities. Since there are different methods to test these junctions, I want to briefly discuss the benefits and weaknesses of the most commonly used API testing methods in this article.

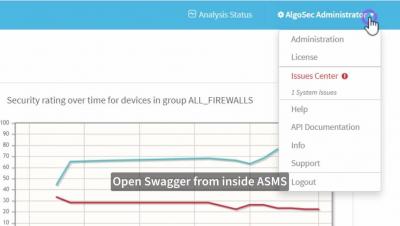
AlgoSec API Swagger

On premise and in the cloud, AlgoSec simplifies and automates network security policy management to make your enterprise more agile, more secure and more compliant – all the time. The AlgoSec platform provides a set of Swagger API documentation, available right from the platform itself. Swagger enables you to execute API request calls and access lists of requested parameters.

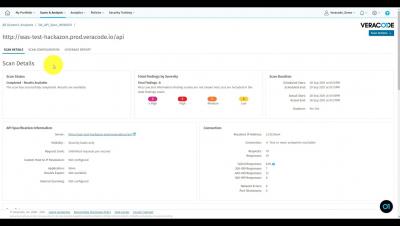
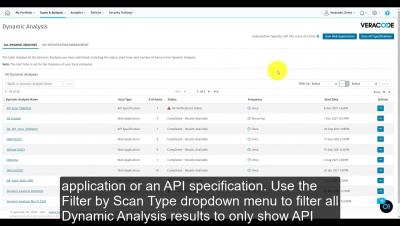
Review API Scanning Results

In this video, you will learn how to review Dynamic Analysis scan results for an API specification. After creating and submitting a Dynamic Analysis API specification scan, you can return to the list of Dynamic Analyses at any time to check for status updates and to view results. Please note, you must have the Creator, Reviewer, or Security Lead role to be able to view the results of a Dynamic Analysis, unless the results are linked to a Veracode application profile for which you have permission to view.

Review API Scanning Prescan Results

In this video, you will learn how to review Dynamic Analysis prescan scan results for an API specification. After creating and submitting a Dynamic Analysis API specification scan, you can return to the list of Dynamic Analyses at any time to check for status updates and to view results. Please note, you must have the Creator, Reviewer, or Security Lead role to be able to view the results of a Dynamic Analysis, unless the results are linked to a Veracode application profile for which you have permission to view.