Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From Agent Discovery to Agentic Exposure Response: Reco + Seemplicity

Copilots and assistants shipped into apps you own, agents reaching in through MCP servers and OAuth tool grants, and the service accounts and tokens they all run as. Almost none of it went through a review. This Reco + Seemplicity integration closes the gap between finding an exposed agent and fixing it. Reco discovers every agent operating across your apps, what data it reaches, and what actions it takes.
Why AI Coding Agents Keep Writing Broken Access Control

AI coding agents produce authorization logic that compiles, passes review, and enforces the wrong policy. Broken access control ranks first in the OWASP Top 10:2025, where 100% of applications tested showed some form of it, across 1,839,701 recorded occurrences, the highest count of any category on the list. One part of that category is also the part that pattern-based scanning was never built to reach.

Next.js CVE-2026-94545: Critical ImageResponse Vulnerability Enables RCE via SVG

A critical remote code execution vulnerability was disclosed in Next.js on September 22, 2026, and an out-of-band security update was released to fix it. CVE-2026-94545 is a remote code execution vulnerability in next/og, the feature Next.js applications use to generate images on demand. The GitHub advisory rates it 9.5 on CVSS v4.0. An unauthenticated attacker can reach it over the network, and the root cause is an upstream SVG-escaping vulnerability that applications inherit without realizing it.

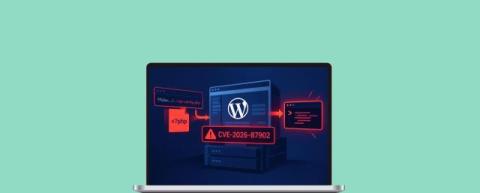
WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours

WordPress patched CVE-2026-87902 on September 22, 2026. Attackers were exploiting it the same day. Within hours of disclosure, attackers progressed from reconnaissance to active exploitation attempts, including attempts to write malicious PHP files to disk. The vulnerability is critical, with a CVSS v4.0 score of 9.2. Unauthenticated attackers can exploit it remotely. A public scanning template is already in circulation, and CISA has added the vulnerability to its KEV catalog.

Zero-Day Attack Prevention: Catching Unknown Vulnerabilities Before Threat Actors Do

On September 1, 2026, OpenAI announced that its Astra model had reached the Critical tier for cyber capability under the company’s Preparedness Framework, a first for its systems. While working through an internal benchmark of 20 recently disclosed vulnerabilities in Google’s V8 engine, the model found two zero-days that no one had asked it to look for and used them in a working exploit chain. OpenAI is disclosing both flaws and restricting the capability to vetted testers.

Emerging Threat: (CVE-2026-86858) ServiceNow AI Platform Unauthenticated Privilege Escalation via GraphQL

CVE-2026-86858 is an improper access control flaw in the ServiceNow AI Platform, classified as CWE-284. ServiceNow describes it as an unauthenticated privilege escalation reachable through GraphQL. In certain circumstances an unauthenticated user can create, modify, or delete instance data beyond what was intended. The vulnerability carries a CVSS v4.0 base score of 8.7 (High). Attack vector is network, attack complexity is low, and neither privileges nor user interaction are required.

What Is Agentic AppSec?

Agentic AppSec (agentic application security) is the practice of using a team of AI security agents to run an organization's entire application security program: understanding the application, modeling its threats, finding the vulnerabilities that matter, deciding what is worth fixing, generating and validating fixes, and proving those fixes hold. It applies continuously to both new code and the existing backlog.

Critical Citrix NetScaler ADC and Citrix NetScaler Gateway Vulnerabilities

On September 27th 2026, Citrix disclosed multiple vulnerabilities affecting NetScaler ADC and NetScaler Gateway. Arctic Wolf tracking indicates that CVE-2026-88771 and CVE-2026-88772 have been exploited in attacks against NetScaler devices as zero-days. Additional CVEs are also disclosed in the Citrix Security Bulletin. CVE-2026-88771 is an unauthenticated remote code execution vulnerability caused by improper input validation that can allow arbitrary command execution.

Beyond the Scanner: How Verified PoC exploits Prove True Business Risk

On September 1, OpenAI announced that its new model, GPT-6 Astra, had become the first to cross the “Critical” cybersecurity threshold in the company’s Preparedness Framework. Most coverage focused on the safety implications, and fairly so, but buried in the announcement sits a benchmark result that should change how every security leader reads their next vulnerability report.