Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Deployment alerts: know when a renewed certificate doesn't land

Renewing a certificate is the easy part. Getting it onto the server is where automation breaks. Somebody rotates the API token on the firewall. A service account password expires. A VM gets rebuilt and the agent never comes back. The certificate renews right on schedule, the deployment fails, and the server keeps serving the old certificate until it expires. Renewed and deployed are not the same thing.
The Cost of a Mid-Market Ransomware Attack

The extortion demand is the figure that gets quoted and rarely the largest line. Downtime, restoration, forensics, legal hours and notification each contribute, and for a mid-market company the regulatory components behave in a way that catches finance teams out. ‍ Reporting deadlines do not scale with headcount.

The Best AI Governance Platforms for Mid-Market Companies

Enterprise AI governance guidance assumes a review board that meets monthly, an independent validation function, an impact assessment per system and somebody whose job title contains the words AI and compliance. A company of three hundred people has none of those and is governed by the same regulations. ‍ The difference runs deeper than budget. Enterprise programs are assessment-led, which scales with headcount because every system needs an assessor.

How AI Audit Trail Confidence Grows With Each Connected Source

An audit trail is usually judged by how much it contains. The more useful question is how many innocent explanations it rules out, because a record that admits a benign reading supports an assertion rather than a conclusion. ‍ Each source added to a trail removes an alternative explanation rather than adding detail. Confidence therefore climbs in steps rather than smoothly, and three sources of the same kind are worth less than two of different kinds. ‍

iGaming Fraud Detection: How to Identify Risk Before Player Accounts Are Compromised

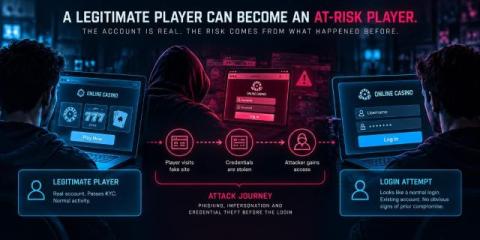
iGaming fraud detection already spans much of the player journey, from registration and identity verification to login, payments and account activity. But for phishing-driven account takeover (ATO), an important part of the risk can develop before suspicious activity appears inside the operator environment. That distinction matters as operators try to improve fraud detection without adding unnecessary friction.

NIS2 Part One: Why Your NIS2 Supply Chain Strategy Is Already Falling Short

Tens of thousands of European organizations are legally accountable for the security of companies they do not control but on whose services they rely. Under Article 21(2)(d) of the NIS2 Directive, any in-scope entity is required to manage supply chain security, including the security aspects of its relationships with its direct suppliers and service providers. Article 21(3) further specifies that an organization must take each supplier’s specific vulnerabilities into account.

Warning: Phishing Attacks Are Using AI-Themed Ad Lures

A phishing campaign is using AI-themed lures to target employees who operate advertising accounts, according to a new report from Island. The campaign is launched from a phishing platform that poses as a portfolio of AI advertising tools, using branding from Gemini, Claude, ChatGPT, Perplexity, and Muse. The platform’s operator added a fake Muse Ads lure eight days after Meta launched its Muse AI agent.

Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

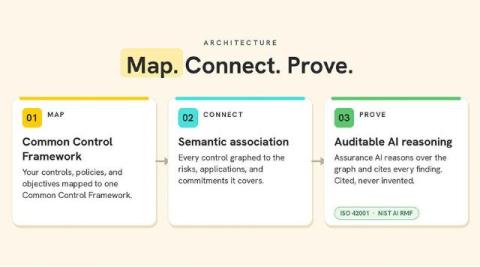
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.