Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Incident Response Automation Helps Organizations

As digital transformation opportunities are constantly expanding, cyber threats are becoming more dangerous day by day. And as a result of this, it’s getting increasingly harder to secure digital assets. Cybersecurity teams must constantly improve their nstrategy repertoire so that organizations do not face severe losses. Incident response strategies stand out as one of the most powerful weapons that can prevent cyber attacks.
Introducing Change Control

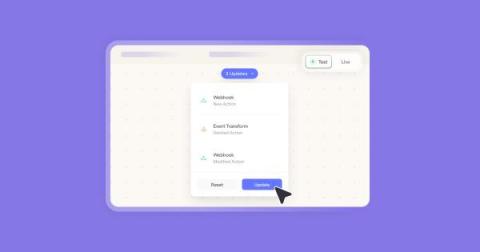
Companies depend on Tines to automate their mission-critical security workflows. We take this responsibility extremely seriously, and we’re always enhancing our platform’s capabilities to make it even more trustworthy and reliable. Today, we introduced Change Control. When enabled, it adds a test environment to your Story, allowing you to prototype and experiment with changes, before applying them to your Story.

TripActions' Aaron Cooper: Why understanding broader company culture is critical to a security team's success

Aaron Cooper is the Security Operations Manager at TripActions with 20+ years of experience working in a variety of enterprise infrastructures. He specializes in managing and designing secure network environments to meet the needs of financial and corporate customers, managing security operations centers, and designing and implementing highly secure and available data networks while maintaining HIPAA, SOX, and PCI compliance.

Keeping Your Organization Secure with Limited SOC Resources

Organizations face a growing threat from cybercriminals while struggling to find qualified security professionals who can protect their infrastructure and sensitive data. This blog will explore the concept of a Security Operations Center (SOC) and the role of SOC analysts in securing your organization. We will also discuss how your organization can leverage automation to improve SOC effectiveness and fill in the gaps when you cannot support a full staff of security professionals.

Doubling down on our mission: Extending our Series B

It’s a challenging time for a lot of businesses right now and we’ve yet to see the full impact of the global economic slowdown. With that, we feel fortunate to be in a position to double down on our mission to help new and existing customers unlock the power of automation, and move from reactive to proactive. In short, Tines has raised an additional $55 million in new funding, led by Felicis, alongside our existing investors Accel, Blossom Capital, Addition, and Lux Capital.

Unlock the Power of Automation: Vulnerability Management

We’ve spoken extensively about the importance of taking a data-driven approach to Vulnerability Management. In short the efficiency and effectiveness of vulnerability management processes depend heavily on inclusion of threat intelligence for both prioritization and response activities. At any given time, only a small fraction of existing vulnerabilities are actively exploited or exploitable.

How Wiz and Torq Combine to Mitigate Existential Cloud Security Threats

A single cloud security incident can stop an enterprise in its tracks, sometimes resulting in irreparable damage to its operation, reputation, and customer loyalty. One key strategy for preventing such incidents is combining complementary cybersecurity tools to defeat threats at scale. A coherent Cyber Security Incident Response Planning (CSIRP) approach requires enterprises to select and integrate the right tools before a security incident occurs.