Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Reach Security Solves Problems That Aren't Sexy | Garrett Hamilton

"The problems we solve are not sexy." But they are hyper-relevant and important. Garrett Hamilton joined Moudy Elbayadi, Ph.D. on Inflection Point: Digital Intelligence Podcast. He explains why Reach goes after problems that have been around for decades, that matter, and that nobody wants to own. He covers why these problems have lasted so long and why they are now possible to fix at scale.

Uncovering indirect attack paths to virtualized domain controllers in Azure

Within Netwrix Security Research, we were helping a customer with an Entra ID assessment and knew they'd already done AD tiering on-prem. We also knew they had domain controllers virtualized in Azure, but it was hard to tell which Windows Server was actually a DC. We figured out that Azure Run Command lets you run commands as SYSTEM, so we used that to do reconnaissance and identify the DCs.

Copilot broke your insider threat detection, and MITRE wrote the proof

MITRE ATT&CK's detection analytic for adversaries mining SharePoint describes bulk access to files and metadata in a short window by privileged or rarely used accounts. That is also a description of Microsoft 365 Copilot answering a question. The technique hasn't changed, but the baseline has, and the exposure now happens with no vulnerability, no compromised credential, and no malicious intent anywhere in the chain.

The water system attacks were simple. Securing OT isn't.

Recent cyberattacks against U.S. water and wastewater systems have put some familiar operational technology (OT) security problems back in the headlines. Federal agencies have warned about malicious actors targeting internet-facing programmable logic controllers (PLCs), changing device configurations, and disrupting operations at utilities across multiple states.

Sophisticated Phishing Operation Continues to Thrive Following FBI Takedown

China-based cybercriminals are using a sophisticated phishing-as-a-service platform called the “Outsider Phishing Kit” to launch massive phishing campaigns around the world, according to researchers at Group-IB. “The scale of this operation is staggering,” the researchers write. “From December 2025 to May 2026, Group-IB has identified over 100,000 phishing pages targeting 54+ countries, leveraging 267 (and growing) phishing templates.

How Astra Security Combines Generative Reasoning with Expert Validation

Every security vendor’s homepage now says “AI-powered” somewhere above the fold, and most are describing the same scanners they sold in 2022 with a model bolted onto the reporting layer. Buyers have noticed, and the skepticism is earned. When everything claims to be intelligent, the label stops conveying information. A security lead evaluating tools is left with one question that matters: whether the tool can actually think through an attack the way a pentester does.

Red Hat OpenShift on IBM Cloud: What It Is and What's New

Running Kubernetes in production takes real work. Patching control planes, managing upgrades, and keeping clusters highly available pulls engineers away from shipping applications. Red Hat OpenShift on IBM Cloud removes that operational load. IBM runs the platform as a fully managed service, and your team keeps its attention on workloads.

Securing what your Bedrock AgentCore agents actually do

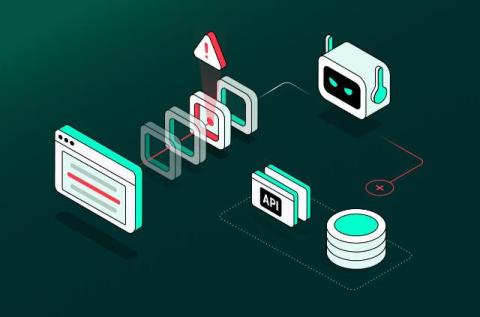
An AI agent is software that can act on your behalf. It may read documents, emails, and web pages, then use the systems you connected to complete a task. Amazon Bedrock AgentCore makes these agents faster to build and deploy. But securing them requires more than limiting which systems an agent can access. You also need to consider what the agent can read once it gets there. A document, email, or web page may contain hidden or malicious instructions designed to influence an agent’s next action.