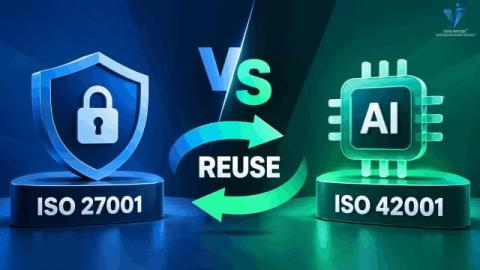
If your organization already operates a mature ISO/IEC 27001 Information Security Management System (ISMS), you are not starting ISO/IEC 42001 from zero. Governance routines, document control, competence management, internal audit, management review, corrective action and parts of your risk and supplier processes may provide a useful foundation. But ISO/IEC 42001 is not an AI extension to ISO/IEC 27001.