Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

When a $1 million hacker bounty becomes a cybersecurity warning

A reported $1 million reward for information that could identify an alleged hacker is the kind of number that grabs attention. But the more important story for security teams is what sits behind the headline: Attackers continue to pursue access to financial accounts, identities and credentials, and organizations need defenses that assume those attacks will keep coming.
Stopping candidate fraud with Persona's head of talent

Recruiters everywhere are seeing hundreds, if not thousands, of fake candidates, and it goes well beyond AI-polished resumes. Natalie, Persona's head of talent, talks with Michael, an account executive on Persona's Workforce Identity team, about what candidate fraud looks like from the recruiter's chair, why Zoom interviews and flying people on site aren't enough, and what changed after Persona added automated identity verification to its own hiring process.

The EU Cyber Resilience Act puts product makers on a 24-hour clock

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Cyberattacks hit grocery retail, exposing supply chain risk

In October 2026, Reuters reported that supermarket operator Ahold Delhaize still had websites and apps offline five days after a cyber incident. Coverage from The Packer framed the wider issue around the cold chain and produce security, while Fox News highlighted the effect on major U.S. grocery chains. The latest cyber incidents affecting grocery retailers are a useful reminder that the impact of an attack is measured in more than encrypted endpoints or exposed data.

PHP2Shell Won't Be the Last. Here's Where the Next One Will Show Up First.

On October 17, Amazon's honeypot network logged a PHP2Shell exploitation attempt from an anonymized IP address. Yet, public disclosure was still four days away. By the time PHP got its fixes in on October 21, the technical details had already leaked, proof-of-concept exploits were in wide circulation, and more exploit attempts were being logged left and right.

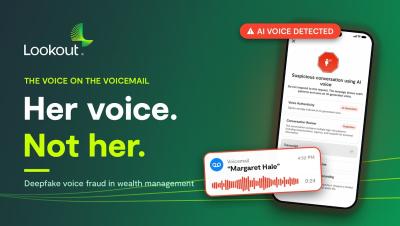
The Voice on the Voicemail: Deepfake Voice Wire Fraud | Lookout

A voicemail from a trusted client. Her voice, her cadence, an urgent $480,000 wire before the cutoff. Except it isn't her. In under 2 minutes, see how AI voice cloning turns a single voicemail into wire fraud, and how a wealth advisor uses Lookout Social Engineering Protection to verify it before the money moves. One voicemail, two outcomes: without Lookout, the wire goes out. With Lookout, the advisor uploads the voicemail to Voice Verifier, sees it flagged as an AI-generated voice and a scam in progress, and calls the client back at her number on file.

Building the Business Case for Agentic AI Security Across EMEA

Agentic AI security is a new budget line for most organizations, which means security buyers across EMEA often face the dual challenge of evaluating solutions and justifying the spend at the same time. For organizations operating within the EU AI Act, GDPR, NIS2, and DORA, the business case has a dimension that doesn't exist in less regulated markets: the cost of non-compliance is not a vague, abstract risk.

The First Questions That Matter: Governing an AI Agent Incident

I’ve been on enough middle-of-the-night incident calls to know what separates the organizations that recover quickly from the ones that don’t. It’s rarely the size of the security budget. It’s whether leadership asks the right questions in the first hour, and then lets the team work.