Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Zero Trust Architecture

Redefining Cybersecurity Perimeters Traditional security models that rely on a defined perimeter are proving to be inadequate in protecting sensitive data and systems. The increasing sophistication of cyber threats demands a more proactive and robust approach. Enter Zero Trust Architecture (ZTA), a paradigm shift in cybersecurity that challenges the conventional notion of trust within network boundaries.
What to Know About Biometric Security

Biometric authentication has emerged as a cutting-edge technology that promises to enhance the accuracy and efficiency of identity verification. Biometrics involves the use of unique physical or behavioral characteristics to confirm a person’s identity, and its applications range from unlocking smartphones to securing sensitive government facilities.

Securing the Internet of Things (IoT)

The Internet of Things (IoT) has emerged as a transformative force, connecting devices, sensors, and systems to enable seamless communication and data exchange. From smart homes to industrial processes, IoT has revolutionized the way we live and work. However, with this proliferation of connected devices comes a significant challenge: ensuring the security of the IoT ecosystem.

Navigating Uncertainty: Why Are Risk Assessments Important for Your Business?

You understand why risk assessments are essential in ensuring success and longevity in the complex business world. A comprehensive understanding of potential hazards and effective mitigation strategies is crucial for safeguarding your organization and achieving a competitive edge. Dive into the fascinating world of risk assessments and discover how they can protect your business from unforeseen threats, enhance decision-making, and ultimately secure your bottom line.

Mastering Your Risk Assessment Report: Steps for Effective Analysis

In today’s rapidly evolving digital landscape, organizations must be vigilant in managing and mitigating cyber risks. One powerful weapon in the cybersecurity arsenal is a comprehensive risk assessment report – a crucial tool for identifying and addressing potential threats. So, how can businesses master risk assessment reports to safeguard their operations effectively?

Applied Lessons from Product Security Teams in Vulnerability Management | Nucleus Security

Product security and vulnerability management have become critical components of an organization's overall cybersecurity strategy. However, these two teams often face challenges in working together effectively, leading to misalignment and potential security gaps. Patrick Garrity hosted a roundtable discussion with industry experts Matthew Clapham and Scott Kuffer to share applied lessons from product security teams and vulnerability management.

The Rise In Vulnerability Disclosure, Exploitation and Threat Intelligence

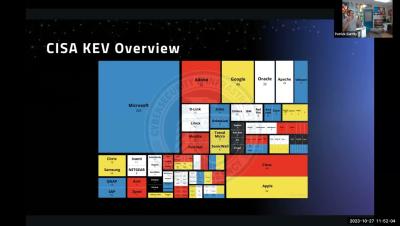
Patrick Garrity, Security Researcher at Nucleus Security, discusses the rise of vulnerabilities exploitation and threat intelligence in the field of vulnerability management. He highlights the history of vulnerability management, the increase in vulnerabilities and exploitation, the limitations of the common vulnerability scoring system (CVSS), and the emergence of vulnerability threat intelligence. Patrick also emphasizes the importance of open-source intelligence, such as CISA's Known Exploited Vulnerabilities (KEV) List and the Exploit Prediction Scoring System (EPSS), as well as the value of commercial threat intelligence.

How Does NIST's AI Risk Management Framework Affect You?

While the EU AI Act is poised to introduce binding legal requirements, there's another noteworthy player making waves—the National Institute of Standards and Technology's (NIST) AI Risk Management Framework (AI RMF), published in January 2023. This framework promises to reshape the future of responsible AI uniquely and voluntarily, setting it apart from traditional regulatory approaches. Let's delve into the transformative potential of the NIST AI RMF and its global implications.

Cyber Regulations in the EU: 5 Proven Strategies for Compliance

The emergence of cyber risk regulations like DORA, NIS2, and PS21/3 signals an imperative need for resilience. In a world where digital disruptions can cripple nations and economies, the industry needed a shift from reactive defence to proactive fortification. CISOs that demonstrate strong cybersecurity leadership, aligning with broader business objectives and proving a positive impact on the organization's bottom line, are better positioned to build trust with stakeholders and minimize cyber risks.

The Evolution of Cybersecurity Education and Training Programs

The significance of cybersecurity has never been more pronounced. As cyber threats evolve and become more sophisticated, the need for robust cybersecurity education and training programs has become paramount. Let’s explore the evolution of cybersecurity education and training, highlighting the growing importance of these programs in developing a skilled workforce capable of protecting against cyber threats.