Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Mobile Security in the Age of Smartphones: Tips for Users and Developers

Smartphones have become ubiquitous with today’s digital world, serving as a central hub for personal and professional activities. This widespread use has escalated the importance of mobile security, making it a critical concern for both users and developers. As cyber threats evolve, so does the need for robust mobile security measures.
Critical Infrastructure Protection: Cybersecurity in the Public Sector

Protecting critical infrastructure has become an indispensable aspect of national security and public welfare. Critical infrastructure, encompassing essential systems such as power grids, transportation networks, water supply systems, and communication channels, forms the backbone of a nation’s economy, security, and health.

GDPR and Beyond: Data Privacy Regulations in a Global Context

Data privacy has emerged as a paramount concern, transcending borders and industries. The introduction of the General Data Protection Regulation (GDPR) by the European Union marked a significant milestone in the global data privacy landscape. However, the conversation around data privacy extends far beyond GDPR, encompassing various regulations worldwide.

Incident Response Planning: A Crucial Component of Cybersecurity

In today’s rapidly evolving digital landscape, incident response planning has emerged as a pivotal aspect of cybersecurity. With the increasing frequency and severity of cybersecurity breaches, organizations are recognizing the importance of being well-prepared and responsive in the face of such threats. Let’s look at the critical role of incident response planning and how it can safeguard your business from rising cyber insurance premiums, reduced coverage, and other potential risks.

Cybersecurity in Healthcare: Balancing Innovation and Patient Data Protection

The healthcare sector stands at a crossroads where innovation and technology are drastically reshaping patient care, yet simultaneously, it faces the increasing challenge of protecting sensitive patient data. As healthcare organizations adopt advanced technologies like electronic health records (EHRs), telemedicine, and AI-driven diagnostics, the need for robust cybersecurity measures becomes paramount.

Supply Chain Cybersecurity: Ensuring the Security of the Digital Ecosystem

The digital ecosystem is an intricate web of interconnected technologies and processes. Within this network, supply chain cybersecurity has emerged as a critical component to safeguard against the growing threat landscape. As supply chains become increasingly digital, they also become more vulnerable to cyber attacks that can disrupt operations and compromise sensitive data.

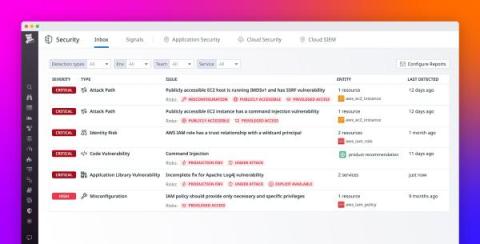
Easily identify and prioritize your top security risks with Datadog Security Inbox

In today’s complex cloud environments, security and engineering teams need to manage vulnerabilities and misconfigurations across multiple layers of the stack, including cloud resources, clusters, containers, and applications. Often, this results in a lengthy list of problems that lacks prioritization and is daunting for users to address.

Top 5 Open Source Security Risks IT Leaders Must Know

Lurking in the open source software (OSS) that pervades applications around the world are open source security risks technology leaders must be aware of. Software is one of technology’s most vulnerable subsets with over 70% of applications containing security flaws. Here are the open source security risks IT leaders must be aware of to protect technology and help it scale safely.

Enterprise Software Security: Challenges and Best Practices

In an age where digital information is critical, enterprise software security is more important than ever. As organizations increasingly rely on complex software systems to manage their operations, the risks and vulnerabilities associated with these systems are growing. This article examines the key challenges in enterprise software security and outlines best practices for mitigating these risks.

C-Suite Liability & Cybersecurity: Navigating a New Era of Enforcement

Author: Owen Denby, General Counsel, SecurityScorecard On October 30, 2023, the SEC charged both SolarWinds and their CISO Tim Brown with defrauding investors, by failing to make disclosures about cybersecurity issues and vulnerabilities related to the massive nearly two-year long “SUNBURST” hack of the company.