Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Open-Source Paradox: Navigating the New Frontier of AI Supply Chain Risk

The recent developments surrounding vulnerabilities in major AI repositories like Hugging Face serve as a critical wake-up call for the cybersecurity community. As we accelerate toward an agentic future, the platforms we rely on for innovation are increasingly becoming the primary vectors for systemic risk.

Top 10 Open Source SIEM Tools for 2026

At 2 a.m., an alert queue full of raw Windows events, firewall logs, and duplicate detections stops being a tooling problem and becomes an operations problem. The team does not need another dashboard. It needs a SIEM that can ingest the right data, normalize it, correlate it well enough to surface real incidents, and stay maintainable after the initial rollout.

Inside Modern Cybersecurity Companies: How Businesses Are Defending Email and Critical Infrastructure

Every business now depends on connected systems to communicate, store information, manage operations, and support customers. Email platforms handle sensitive conversations, Linux servers power cloud environments, and digital infrastructure keeps websites, applications, and internal networks running around the clock. While these technologies create efficiency and scalability, they also create opportunities for attackers looking to exploit weak points.

Protestware by open source maintainer to hinder agentic coding: The jqwik 1.10.0 Prompt Injection

On May 25, 2026, the maintainer of jqwik, a Java property-based testing library, released version 1.10.0 to Maven Central with a hidden instruction intended for AI coding agents. The payload told agents to disregard previous instructions and delete all jqwik tests and code. It was hidden from humans with ANSI terminal codes but left fully readable to any tool that captures raw output.

Commercial vs Open Source AI Attack Detection Tools: A Buyer's Guide

If you’re weighing open source against commercial tools for detecting attacks on your AI agents, you’re probably trying to answer a single question. Can we build this ourselves, or should we buy it? It’s a fair question, and the existing content on it isn’t much help. Most comparisons line up tools side by side and tally features. That tells you which tool is better at one slice of the problem. It doesn’t tell you whether you have a working detection program.

Qinglong task scheduler RCE vulnerabilities exploited in the wild for cryptomining

In early February 2026, users of Qinglong (青龙), a popular open source timed task management platform with over 19,000 GitHub stars, began reporting that their servers were maxing out CPU usage. The cause was a cryptominer binary called.fullgc, deployed through two authentication bypass vulnerabilities that allowed unauthenticated remote code execution. The attacks went largely unnoticed in the English-speaking security community.

Episode 13 - Battle-Hardened Research: Navigating the Intersection of AI and Open Source

Richard Bejtlich sits down with Ali Islam to pull back the curtain on how a security research lab functions within a modern security company. Moving beyond the "ivory tower" of academia, Ali explains why researchers must be battle-hardened by real-world threat actor techniques to remain effective in the field. The conversation dives into Corelight’s unique commitment to the open source community through the direct funding of Zeek and Suricata developers, ensuring that community-driven tools can scale to meet massive enterprise traffic demands.

MyClaw Detailed Review: Is This OpenClaw Managed Hosting Worth It?

I've been working in the AI tools space for a while now, and one thing that comes up repeatedly is the gap between open-source AI frameworks and the actual effort required to run them. OpenClaw is a great example - powerful, flexible, and genuinely useful for building AI agents. But getting it deployed and keeping it running? That's a different story. That's what led me to try MyClaw AI. Here's an honest look at what the platform actually offers, who it's for, and whether it's worth the cost.

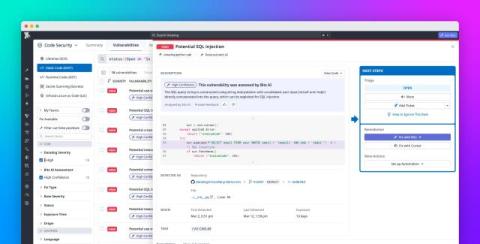
Introducing our open source AI-native SAST

Static application security testing (SAST) tools help developers quickly catch potential vulnerabilities as they code. However, these tools rely on inflexible rules that often generate a high number of false positives, reducing trust in their accuracy and slowing adoption. To help developers access context-aware vulnerability detection, we’ve released an open source AI-native SAST solution. This tool scans code changes incrementally and surfaces security issues in real time.