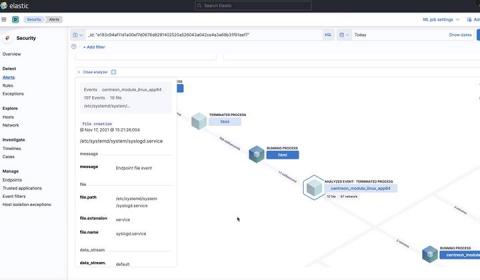
That’s right all, it’s time for the latest MITRE Engenuity ATT&CK® evaluation. As we have come to expect each year, Elastic — along with other security vendors — are evaluated by MITRE Engenuity, a tech foundation that brings MITRE research to the public. The evaluation focuses on emulating techniques from the MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) framework to assess vendor protection capabilities.
As the conflict in Eastern Europe continues, the Splunk Threat Research Team (STRT) is constantly monitoring new developments, especially those related to destructive software. As we have showcased in previous releases in relation to destructive software and HermeticWiper, malicious actors modify their TTPs in order to become more effective and achieve their objectives.
CrowdStrike data science researchers recently explored and experimented with the use of Bidirectional Encoder Representation from Transformers (BERT) for embedding command lines, focusing on anomaly detection, but without detailing the model itself. Diving deeper into that research, CrowdStrike researchers explain the reasons for using BERT for command line representation and how to train the model and assess its performance.
Ransomware isn’t just an internal threat for your organization, it’s also a global crime, and data breach notifications are governed by various laws, policies, and agencies. Let’s go over some common cyber-compliance questions about ransomware, data breach notification and reporting, and the laws that cover cybercrime.
The Splunk Threat Research Team is actively monitoring the emergence of new threats in the cyber domain of ongoing geopolitical events. As we have shown previously in several releases, including HermeticWiper and CaddyWiper, actors in this campaign are deploying, updating, and modifying stealthier malicious payloads. On March 17th, 2022, the Ukraine CERT discovered a new malicious payload named DoubleZero Destructor (CERT-UA #4243).
Appending a malicious file to an unsuspecting file format is one of the tricks our adversaries use to evade detection. Recently, we came across an interesting email campaign employing this technique to deliver the info stealer Vidar malware. First, let’s examine the email delivery mechanism, then go on to take a closer look at the Vidar malware itself. Figure 1: The malicious spam message The messages in this campaign have two things in common.