Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Call Is Coming from Inside the House: CrowdStrike Identifies Novel Exploit in VOIP Appliance

CrowdStrike Services recently investigated a suspected ransomware intrusion attempt. The intrusion was quickly stopped through the customer’s efforts and those of the CrowdStrike Falcon Complete™ managed detection and response (MDR) team, which was supporting this customer’s environment.
Threat Update: Industroyer2

The Splunk Threat Research Team (STRT) continues to monitor new relevant payloads to the ongoing conflict in Eastern Europe. One of these new payloads was found by the Ukranian CERT named “Industroyer2.” The name of this new payload references the original "Industroyer" malicious payload used against the country of Ukraine's power grid in 2016 and allegedly was able to affect a fifth of the power capacity of the city of Kyiv.

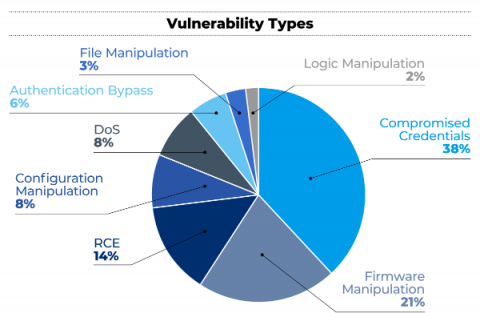
OT:ICEFALL: 56 Vulnerabilities Caused by Insecure-by-Design Practices in OT

It has been 10 years since Project Basecamp, a research project conducted by Digital Bond that investigated how critical operational technology (OT) devices and protocols were, to use the term they coined, “insecure by design.” Since then, we have seen hugely impactful real-world OT malware such as Industroyer, TRITON, Industroyer2 and INCONTROLLER abusing insecure-by-design functionality.

How to stop sophisticated ransomware attacks

The number and frequency of ransomware cyberattacks are growing every year. The European Union Agency for Cybersecurity (ENISA) recorded a 150% increase in 2020 alone and, as of last year, ransomware attacks have become the number one threat. Added to this, the recovery costs and downtime incurred can be up to 10 to 15 times higher than the ransom demanded by cybercriminals.

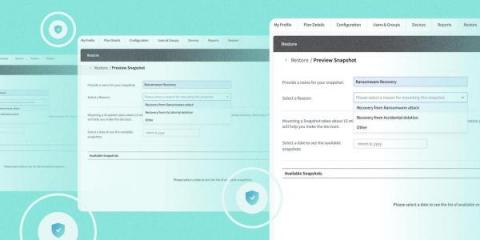
How Egnyte Built Snapshot Recovery to Mitigate Ransomware Attacks

As companies accumulate and store large amounts of business data in the cloud, data security and governance become a major concern. More than 16,000 companies use Egnyte to manage, secure, and govern their content. These businesses rely on the unified platform to keep their business running smoothly, because data loss due to ransomware attacks or accidental file deletion could have profound impacts on their bottom lines.

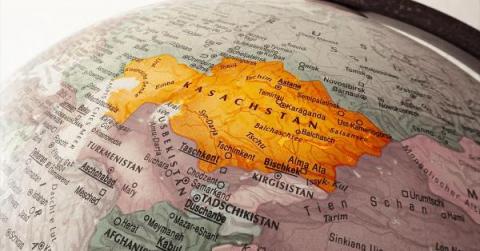
Lookout Uncovers Hermit Spyware Deployed in Kazakhstan

Lookout Threat Lab researchers have uncovered enterprise-grade Android surveillanceware used by the government of Kazakhstan within its borders. While we’ve been following this threat for a while using Lookout Endpoint Detection and Response (EDR) these latest samples were detected in April 2022, four months after nation-wide protests against government policies were violently suppressed.

Royal Flying Doctor Service Queensland Protects The Crown Jewels of Patient & Aviation Data

Royal Flying Doctors Service Queensland has protected business-critical data and ensured its life-saving operations are available 24/7 with Rubrik. As both a healthcare and aviation organisation, it needed to ensure sensitive patient data and key aviation data were protected from the increasing threat of ransomware targeting the healthcare sector.

How Rubrik Supports the NIST Cybersecurity Framework Profile for Ransomware Risk Management

Rubrik was built on a foundation of Zero Trust architecture. The National Institute of Standards and Technology (NIST) is a United States federal agency that works with organizations of all sizes to help them implement cybersecurity best practices.