Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CrowdStrike Delivers the Next Evolution of the Agentic SOC

The average adversary breakout time is now 29 minutes, with the fastest recorded at 27 seconds, according to the CrowdStrike 2026 Global Threat Report. AI is supercharging the adversary playbook, empowering many to move faster across multiple domains. Defenders must match that speed with AI-driven security operations that investigate and respond across every domain, in real time.

CISO Risk Intel Brief: Edge Zero-Days, Artifact-Repository Takeover, and Identity-Pivoted Extortion

This CISO application risk intelligence briefing covers two distinct horizons: the past seven days (Wednesday, 26 August 2026 through Wednesday, 2 September 2026) and the preceding thirty days (Sunday, 3 August 2026 through Wednesday, 2 September 2026). It is written for board risk committees and operating CISOs.

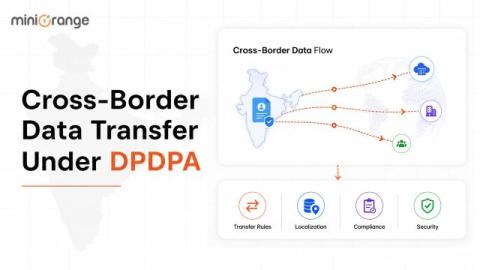
Cross-Border Data Transfer Under India's DPDPA

Businesses operating across countries routinely move personal data between India and overseas systems. Customer information may be stored by a global cloud provider, employee records may be accessed by an international headquarters, or an Indian business may use SaaS platforms whose infrastructure is located outside the country.

AI Governance Auditing for Security and IT Teams

AI governance auditing distinguishes between a documented policy and a working control. The audit traces one AI output back through the identity that invoked it, the data it reached, the guardrail that applied, and the record retained afterward. Most programs fail because access is ineffective: nobody can say which identities access sensitive data through an AI assistant, let alone prove the limit is held.

Microsoft Entra ID monitoring: Detecting suspicious activity

Entra ID monitoring correlates sign-in, audit, and privileged-role activity to expose suspicious identity changes while evidence still exists. Native controls leave gaps in retention, licensing, and correlation, so resilient teams export data, baseline admin behavior, and connect to Entra ID, Privileged Identity Management (PIM), OAuth, Conditional Access, and on-premises Active Directory events in a single workflow.

Extending the Single Source of Truth to the Agentic Software Supply Chain

Every developer on your team now runs multiple agents. None of them are waiting for human sign-off to act. That’s exactly the gap we discussed and closed at swampUP 2026. JFrog unveiled new capabilities that extend the JFrog Platform as not only the Single Source of Truth for OSS and heritage software, but now the Agentic Software Supply Chain. Here’s everything we announced, and why it matters.

Every New Compliance Framework Restarts the Same Fire Drill. It Doesn't Have To.

Every compliance audit starts the same way: Someone flags a deadline, the team scrambles to pull evidence, map controls, and prove that the policies running in production actually match what the framework requires. They make it through. They exhale. Six months later, a new framework arrives, and the fire drill starts all over again. Most teams walk away from an audit believing they are compliant.

Governance Strikes Back: The Most Used, Most Abused Word in the Galaxy

Ask AI to Choose a prompt Write a TLDR of this post Explain the security risk Summarize what CISOs should know When I walked to the stage in Copenhagen, I had a lot on my mind. For 3 days I'd had countless conversations with leaders and practitioners about AI and agentic security. The one word on everyone's lips was "governance"; day 3 at the conference was "Governance Day," in fact. This is a bag one vendor was giving out: But governance of what? To what end?

Introducing Subprocessor listing in Trust Center profiles

At UpGuard, we believe your Trust Center should be the single place your prospects and customers go to get their trust questions answered. Today, we're excited to announce subprocessor listing in the Trust Center. This capability lets you publish your subprocessors directly where buyers already look for trust signals. You can also keep that list up to date and enable customers to subscribe to updates.