Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

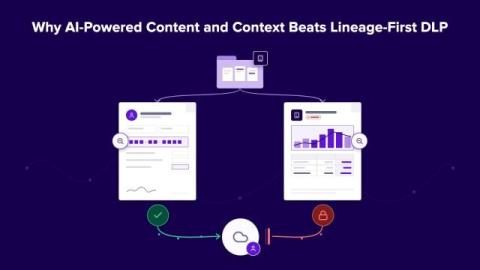
Why AI-Powered Content and Context Beats Lineage-First DLP

The Journey to Autonomous DLP · Context Intelligence Understand the content and the boundary first. History is a secondary factor. Our vision for Autonomous DLP starts with understanding data well enough to make the right decision in real time. What does the document contain? Does it hold the user’s own information, someone else’s records, or confidential company material?
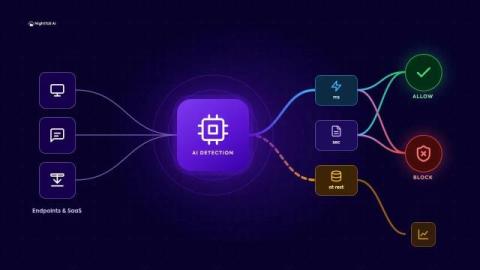
How Nightfall Blocks Data Exfiltration in Milliseconds

Blocking an exfiltration means deciding, in the moment, whether the data leaving a device is sensitive. That turns a detection platform built for accuracy and scale into one that must also answer in milliseconds. Nightfall pioneered the AI-first approach to DLP. Instead of leaning on regular expressions and pattern matching alone, we use language-aware machine learning models that understand the context sensitive data appears in.

Meta Muse in the Enterprise: Data Security for Personal Autonomous Agents

The deployment of personal AI agents like Meta's Muse represents a structural shift in enterprise data loss prevention. Unlike conversational web chatbots where data movement is limited to manual user prompts, autonomous personal agents operate in cloud virtual machines, run continuous background tasks, and connect directly to enterprise SaaS platforms through OAuth integrations.

September 2026 Product Updates

September was the month Nightfall's control layer reached inside the model call. Five releases shipped: Claude Inference Hooks, MCP Gateway, expanded endpoint exfiltration controls, personal file classifiers, and PII coverage across 30 countries. Together they close the gap between what security teams can control when a person moves data and what they can control when an AI agent does.

AI Agent Security Explained: Agents, MCP, Prompt Injection, and the AI Harness

AI Agent Security is quickly becoming one of the most important areas in cybersecurity. Terms like "agent," "harness," "MCP," "tool calls," "tool responses," "instruction hijacking," "indirect prompt injection," "prompt exfiltration," and "tool misuse" are appearing in conference talks, vendor announcements, podcasts, and industry discussions, often without clear explanations.

Nightfall's integration with Claude's Compliance API is now live

What this milestone means for enterprise AI security - and why we built it. AI adoption inside the enterprise didn't slow down and wait for security to catch up. It accelerated. And nowhere is that more visible than in the rapid deployment of large language models like Claude across enterprise workflows. Customer support teams use it to summarize tickets. Legal teams use it to review contracts. Engineers use it to write and review code. Finance teams use it to draft reports.

Why MCP Breaks the Financial Services Security Stack

A relationship manager asks the firm's AI assistant to "summarize my top wealth clients by AUM and flag anyone with a pending transfer over $500K." The agent calls a CRM MCP server, then a core banking MCP server, then a market data MCP server, and returns a clean answer in twelve seconds. Names, balances, account numbers, pending wire details, all rendered in plain text inside the chat window. No file moved. No email left the network. No DLP channel triggered.

CISA's GitHub Leak Is a Preview of the MCP Security Problem Every CISO Is About to Inherit

America's cybersecurity agency left its production credentials sitting in a public GitHub repo for six months. The same failure pattern is now being automated by AI agents in every enterprise running Cursor, Claude Desktop, or Copilot.

What Is MCP Security? 9 Things Every CISO Needs to Know

Your AI agents had a productive day. Nobody can tell you what data they touched. A developer opens Cursor and connects it to a GitHub MCP server and a Postgres MCP server. The agent reads the repo to understand a schema change, finds an AWS access key in a config file, and uses it to run a migration against staging. The key now lives in the agent's context, in the Postgres query log, in the chat history, and in whatever artifact the developer copies out. No alert fired. No policy triggered.