In part 1 of this series, we discussed data privacy, the related laws, and the data collection practices that help comply with those laws. In this blog, we’ll take a look at the challenges in securing customer data and five effective steps to overcome them. Many countries deem data privacy a fundamental human right and have implemented data protection laws.
Authorities that lay down compliance regulations often update them in order to keep them relevant. However, for organizations that fall under the purview of these regulations, it can be a challenge to keep up with the updates and ensure that they stay compliant.
Companies have increasingly allowed bring your own device (BYOD) policies to support remote work, but in today’s cybersecurity landscape, this trend has led to an increased attack surface. Each additional endpoint increases the potential for credentials to be compromised through credential phishing attacks. Hackers are leveraging this trend to conduct insider attacks, leaving businesses vulnerable to data breaches.
Today, we’re excited to share that Zoho (ManageEngine) was positioned as a Leader in three recent IDC vendor assessments for the Unified Endpoint Management (UEM) market: IDC MarketScape: Worldwide Unified Endpoint Management Software 2022 Vendor Assessment IDC MarketScape: Worldwide Unified Endpoint Management Software for Apple Devices 2022 Vendor Assessment IDC MarketScape: Worldwide Unified Endpoint Management Software for Small and Midsize Businesses 2022 Vendor Assessment ManageEngine has a
In the first six parts of this blog series, we laid the foundation for beginning to work with and manage Active Directory (AD). With the groundwork out of the way, it is now time to explore the relationship between cybersecurity and AD. Taking this series one step further, this blog provides an overview of which design considerations are important in securing your AD infrastructure against potential security breaches.
The recently discovered Windows zero-day vulnerability continues to make news as threat actors across the globe are relentless in their efforts to exploit it. The vulnerability, dubbed Follina, can be exploited when the Microsoft Support Diagnostic Tool (MSDT) is called by a Microsoft Office application using the URL protocol.
Security experts around the world are talking about the importance of improving security measures to keep networks safe—and for good reason. We have plenty of examples of how relentless threat actors can be, and we’ve now seen that not even a pandemic can stop or slow down their attacks.
Weeks after President Rodrigo Chaves Robles became Costa Rica’s 49th president, he had to tackle the country’s largest cyberattack ever. Costa Rica declared a state of emergency following a series of detrimental ransomware attacks carried out by the Conti ransomware gang.
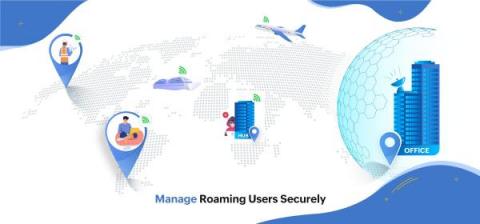
Managing roaming users from a central point has always been daunting. Enterprises found it easy when they had to manage devices inside a network. Having firewalls on either side of the boundaries and restricting susceptible APIs and network packets, businesses found it convenient to manage their devices. Is this a realistic scenario today? Enterprises are evolving. Work patterns have inclined towards modern approaches. Hybrid work patterns are the encouraged mode for working.