Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to secure Exchange Server beyond the CVE-2026-62911 fix

Remote access has always been a core part of how on-premises Exchange works. Users need OWA to read their email from outside the office. Their devices need Autodiscover to set themselves up automatically. Keeping both reachable means keeping Exchange accessible from the Internet, and that opens up more of the server than most organisations realise. CVE-2026-62911 is the latest example. Microsoft released the fix on August 11, 2026.
Agentic AI for ITOps: Is your organization ready for the security challenges?

AI is set to provide increasing value in IT by enabling more ways to simplify complex IT operations, offering actionable insights, automating routine tasks with context-aware automation, and detecting abnormal events with advanced machine learning algorithms. With agentic AI, systems can understand what is happening in an IT environment, reason about the most probable root causes, determine the right course of action, and implement these changes without requiring additional human intervention.

ManageEngine Listed on the UK Government's G-Cloud 15 Framework

For public sector organisations, digital change is rarely just a question of new tech. It is also about finding solutions that are secure, effective, sustainable, and just as importantly, straightforward to procure. That is why we are delighted to announce that ManageEngine has been awarded a place on the UK Government’s G-Cloud 15 framework, with our cloud applications listed under Lot 2b: Software as a Service (SaaS).

Breach fatigue: Why your team has switched off and how to fix it

Cybersecurity continues to face continued challenges in the Australian environment. The Australian Signals Directorate’s (ASD's) Annual Cyber Threat Report 2024–25 revealed that there were more than 84,700 cybercrime incidents and over 42,500 calls to the Australian Cyber Security Hotline, representing a 16% increase in comparison to the previous reporting period. More threats. More notifications. More training events. Yet, surprisingly, employee vigilance is continually decreasing.

What is a backdoor attack?

A backdoor attack is hard to detect. Since they bypass standard security measures, backdoor attacks can enter your system and go unnoticed for a long time. While some cyberattacks tend to be smash-and-grab, backdoor attacks are stealthier. They allow hackers to enter secretly, gather more secure data than typical attacks, and can cause significant damage. Because they can be so difficult to detect and cause so much damage, you need to know the signs of a backdoor attack and learn how to mitigate it.

Passkeys vs. passwords: The authentication cage match nobody asked for

First things first, let’s be honest about one thing: passwords are terrible. Yet, here we are in 2026, still filling up our password fields with trivial stuff like P@ssw0rd123! and pretending we're being secure. And of course, we reuse the same password everywhere: We scribble it on a sticky note and display it on our cubicle wall for the world to see. But even then, we still forget what it was. So we smash that Forgot Password link so often, we might as well have it bookmarked.

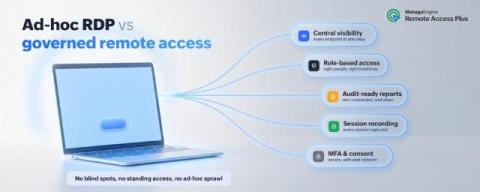
Why unmanaged RDP is risky at enterprise scale (and how to regain control)

Remote Desktop Protocol (RDP) is the path of least resistance for gaining access to another Windows machine. It is built into the OS, it is free, and almost every admin and help desk technician already knows how to fire up mstsc.exe and type in a hostname-as simple as that. That convenience is exactly why RDP is everywhere inside corporate networks.

Top tips: How to spot a scammer pretending to be your boss

Top tips is a weekly column where we highlight what's trending in the tech world and share practical ways to navigate these shifts. This week, we're looking at spear-phishing: how cybercriminals weaponize social engineering, why your natural instinct can act as a security blind spot, and practical steps to verify suspicious requests before you take action. I would like to make a confession: I’m a well-versed tech expert, but I almost fell for a phishing scam.

Segmenting visibility with DNS Views for tighter network access control

Most organizations experience a strange DNS problem at some point: The same domain name means something different depending on who's asking for it. For example, a single internal app, workspace.company.com, might need to serve a locked-down instance to finance, a live staging build to engineering, and a stable production build to support — all under one domain and from the same DNS server.