Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to detect security threats in your systems' Linux processes

Almost all tasks within a Linux system, whether it’s an application, system daemon, or certain types of user activity, are executed by one or more processes . This means that monitoring processes is key to detecting potentially malicious activity in your systems, such as the creation of unexpected web shells or other utilities.

Cybersecurity experts are currently drowning in ransomware attacks

U.S. President Joe Biden is under pressure to take a stand against a relentless pace of cybersecurity attacks. Russian-speaking hackers have claimed accountability for a recent ransomware assault on IT management software provider Kaseya VSA. The group of Russian threat actors also referred to as the Revil Group, launched a bombshell supply-chain hit during the weekend of July 4th, 2021 against Kaseya VSA and multiple managed service providers.

'The Perfect Scorecard' Focuses on Communication Between CISOs and the Board

In most companies today, there is a critical divide between the Chief of Information Security (CISO) and their board of directors. Our new book, The Perfect Scorecard: Getting an ‘A’ in Cybersecurity from your Board of Directors , is an attempt to close that gap. The Perfect Scorecard features insights from 17 leading CISOs and executives known for their leadership skills and their ability to communicate across roles and sectors.

The Cost of a Data Breach Report: Key Highlights

IBM’s Cost of a Data Breach Report 2021 analyzed 537 real breaches and conducted nearly 3,500 interviews to uncover the true cost of a data breach in 2020. The publication covers initial attack vectors, how long it took organizations to discover and contain braces, as well as the effects that incident response efforts and artificial intelligence have on mitigating breach costs.

Cybersecurity Visibility: The Key for Business, Security and SOC Alignment

It has become obvious that visibility is one of the critical pillars for the success of any organization’s cybersecurity program. Research by ESG found that nearly 80% of organizations with a lack of visibility into their assets report roughly three times as many incidents. That sobering statistic is cited in a recent report from SANS, Making Visibility Definable and Measurable, that examines the issue from multiple perspectives.

The anatomy of an arbitrage betting bot

In gaming and betting, it is said that the house always wins. However, some bettors are constantly looking for loopholes to guarantee a profit no matter the outcome of their bets. They have even developed sophisticated software tools to help with a controversial tactic called arbitrage betting, which costs the industry millions each year.

Hunting for Detections in Attack Data with Machine Learning

As a (fairly) new member of Splunk’s Threat Research team (STRT), I found a unique opportunity to train machine learning models in a more impactful way. I focus on the application of natural language processing and deep learning to build security analytics. I am surrounded by fellow data scientists, blue teamers, reverse engineers, and former SOC analysts with a shared passion and vision to push the state of the art in cyber defense.

Enable multi-factor authentication for Outlook Web App logins and secure enterprise emails

In March this year, organizations employing Microsoft Exchange were in for a shock when Microsoft announced that a hacker group was gaining access to organizations’ email accounts through vulnerabilities in its Exchange Server email software. The group tried to gain information from defense contractors, schools, and other establishments in the U.S.

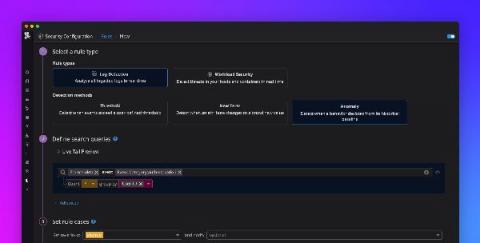
Detect security threats with anomaly detection rules

Securing your environment requires being able to quickly detect abnormal activity that could represent a threat. But today’s modern cloud infrastructure is large, complex, and can generate vast volumes of logs. This makes it difficult to determine what activity is normal and harder to identify anomalous behavior. Now, in addition to threshold and new term –based Threat Detection Rules , Datadog Security Monitoring provides the ability to create anomaly