A new zero day vulnerability actively exploited in the wild has been found in Atlassian Confluence. The vulnerability CVE-2022-26134 affects all supported versions of Confluence Server and Confluence Data Center allowing an unauthenticated user to run arbitrary commands remotely. The Atlassian team confirmed the vulnerability with an official tweet and then also published a security advisory to update its customers.
If you want just to see how to find evidence of the Atlassian vulnerability in your Confluence systems, skip down to the “detections” sections. Otherwise, read on for a quick breakdown of what happened, how to detect it, and MITRE ATT&CK mappings.
Follina—while we’re sure this commune in Italy is lovely, the same can’t be said about this new vulnerability by the same name for InfoSec folks. Thanks to a zero-day bug in the Microsoft Support Diagnostic Tool, Follina is now making the headlines but for all the wrong reasons. This blog talks in detail about the zero-day vulnerability in Microsoft Support Diagnostic Tool (MSDT), popularly known as Follina.
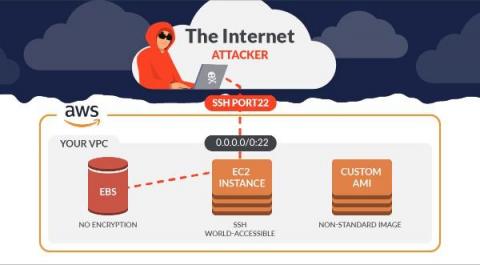
Elastic Compute Cloud (EC2) is arguably one of the most popular AWS services, and really needs no introduction but here is one anyway. With Sysdig, you can secure EC2 by managing configuration and permissions risk, meeting compliance requirements, and managing vulnerabilities on containers and host VMs. When it comes to EC2 and Hosts themselves, Sysdig Secure alerts us in multiple ways.
While living in the 21st century, no one can live off offline modes of payment all the time. Financial institutions, especially banks, have gone the extra mile to ease the process for their clients in the meantime, attracting cybercriminals and their ever-changing malware as threats to their information security. Tinba is one such threat especially plaguing Windows. Read on to know more about the tiny virus and its not so tiny implications.
In this post, we show how enriching Zeek® logs with cloud and container context makes it much faster to tie interesting activity to the container or cloud asset involved.In cloud or container environments, layer 3 networking is abstracted away from the higher-level tasks of running workloads or presenting data. Because of this abstraction, when Zeek logs are collected for cloud or container network environments, the attribution of a network flow to actual workload or application is difficult.
Read also: Chinese hackers are exploiting a Windows MSDT zero-day, Costa Rica’s health service hit by a ransomware attack, and more.
Kroll’s incident responders have seen threat actor groups becoming increasingly sophisticated and elusive in the tactics, techniques and procedures they employ to steal payment card data. One common method is to “scrape” the Track 1 or Track 2 data stored on the card’s magnetic stripe, which provides the cardholder account and personal information criminals need to make fraudulent “card-not-present” (CNP) transactions.