Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Breaking down digital security: What actually matters

We've heard everyone talk about digital privacy, cybersecurity, and how we should set a strong password, but what most people fail to understand is the why. Why is it important to set a strong password? Why do we have to activate two-factor authentication? Why are software updates important? Even though we have a vague idea of why we need to do these things, we really don't know the future implications if we don't secure our digital information.

MCP Gateway Security Controls for AI Agents

The Model Context Protocol states plainly that it cannot enforce these security principles at the protocol level, and that implementors should follow best practices in their integrations. Every control an organization gets therefore comes from where it places the gateway and what it does there. ‍ The protocol publishes its own security best practices document, currently at revision 2026-07-28, naming the attacks a deployment has to handle.

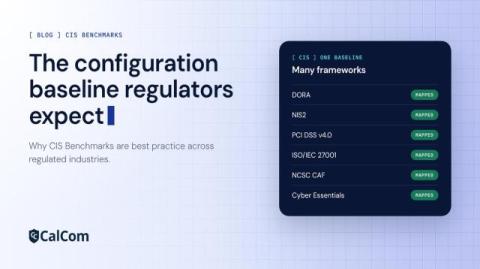
CIS Benchmarks: The Configuration Baseline Regulators Expect

Every major security regulation now asks the same question: can you prove your systems are securely configured? Few of them define what “secure” means. CIS Benchmarks fill that gap. Misconfiguration remains one of the easiest ways into an organisation. Default accounts, legacy protocols and inconsistent settings across thousands of servers hand attackers a foothold. Regulators have noticed.

How to Monitor AI Interactions on Employee Devices

Monitoring has to happen on the device, because three categories of AI use never reach the network in a form anything can inspect. Local models run without leaving the machine. Desktop applications that pin their certificates sit on an inspection bypass list by design. A laptop on a home connection routes through nothing the organization operates at all. ‍ The uncomfortable part is that the first two are deliberate. Somebody approved the bypass, and the approval was correct on its own terms. ‍

Extortion Groups are Impersonating Help Desks to Gain Initial Access

Researchers at ReliaQuest have observed a surge in voice phishing (vishing) and Microsoft Teams phishing over the past several months, particularly from extortion groups like ShinyHunters. “Attackers overwhelmingly targeted users and their unmanaged devices to gain access to accounts,” the researchers write.

Open Banking, Open Doors? API Abuse Through a Threat Intelligence Lens

Open banking drives financial innovation but introduces new cybersecurity risks through APIs, exposed credentials and third-party integrations. Discover how cyber threat intelligence helps financial institutions identify emerging threats, improve visibility and strengthen security.

Acronis Cloud Storage adds a recovery warranty

Backup is not the outcome. Recovery is. When critical data becomes unavailable, businesses need more than a completed backup job. They need confidence that their data is protected, available and ready for recovery. That is why Acronis is introducing the Anti-Ransomware Recovery Warranty for eligible customers using Acronis Cloud Storage. The capability adds a clear recovery commitment to the secure cloud storage foundation customers already rely on.